-- Exhibit -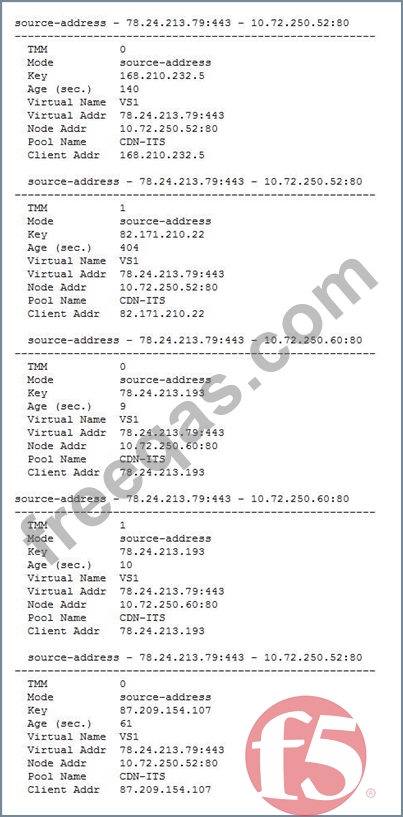
-- Exhibit --
Refer to the exhibit.
A virtual server is set up on an LTM device as follows:
Virtual server address 78.24.213.79
Default Persistence ProfilE. source_addr, 600s.
Pool NamE. Pool1
Pool Members: 10.72.250.52:80 and 10.72.250.60:80 (both on Internal Vlan) There are several current connections to the virtual server, and pool member 10.72.250.52:80 has been set to a
"Disabled" state.
A tcpdump on the Internal Vlan shows traffic going to 10.72.250.52:80.
How soon after the persistence table query was run can existing connections be refreshed/renewed to ensure that no requests are sent to 10.72.250.52?
A BIG-IP Administrator configures remote authentication and needs to make sure that users can still login even when the remote authentication server is unavailable.
Which action should the BIG-IP Administrators in the remote authentication configuration to meet this requirement?
Given the iRule:
when HTTP_REQUEST {
if {([HTTP::username] ne "") and ([HTTP::password] ne "") } {
log local0. "client ip [IP::remote_addr] credentials provided [HTTP::username] [HTTP::password]"} else { pool old_application_pool
}
}
The associated virtual server has a default pool named new_application_pool.
Which functionality does the iRule provide?
In which file would the LTM Specialist find virtual server configurations?
A BIG-IP Administrator needs to find which modules have been licensed for use on the BIG-IP system. In which section of the Configuration Utility can the BIG-IP Administrator find this information?

