FreeQAs
 Request Exam  Contact
  • Home
  • View All Exams
  • New QA's
  • Upload
PRACTICE EXAMS:
  • Oracle
  • Fortinet
  • Juniper
  • Microsoft
  • Cisco
  • Citrix
  • CompTIA
  • VMware
  • ISC
  • SAP
  • EMC
  • PMI
  • HP
  • Salesforce
  • Other
  • Oracle
    Oracle
  • Fortinet
    Fortinet
  • Juniper
    Juniper
  • Microsoft
    Microsoft
  • Cisco
    Cisco
  • Citrix
    Citrix
  • CompTIA
    CompTIA
  • VMware
    VMware
  • ISC
    ISC
  • SAP
    SAP
  • EMC
    EMC
  • PMI
    PMI
  • HP
    HP
  • Salesforce
    Salesforce
  1. Home
  2. Fortinet Certification
  3. FCP_FSM_AN-7.2 Exam
  4. Fortinet.FCP_FSM_AN-7.2.v2026-06-02.q31 Dumps
  • «
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • 7
  • 8
  • »
Download Now

Question 11

Refer to the exhibit.
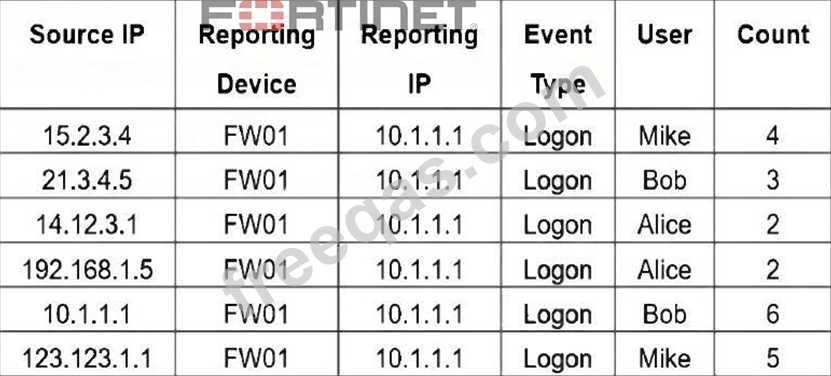
If you group the events by User, Source IP, and Count attributes, how many results will FortiSIEM display?

Correct Answer: B
Grouping by User, Source IP, and Count means that each unique combination of those three attributes will be treated as a separate result. In the table, all six rows have distinct combinations of User, Source IP, and Count - so FortiSIEM will display 6 results.
insert code

Question 12

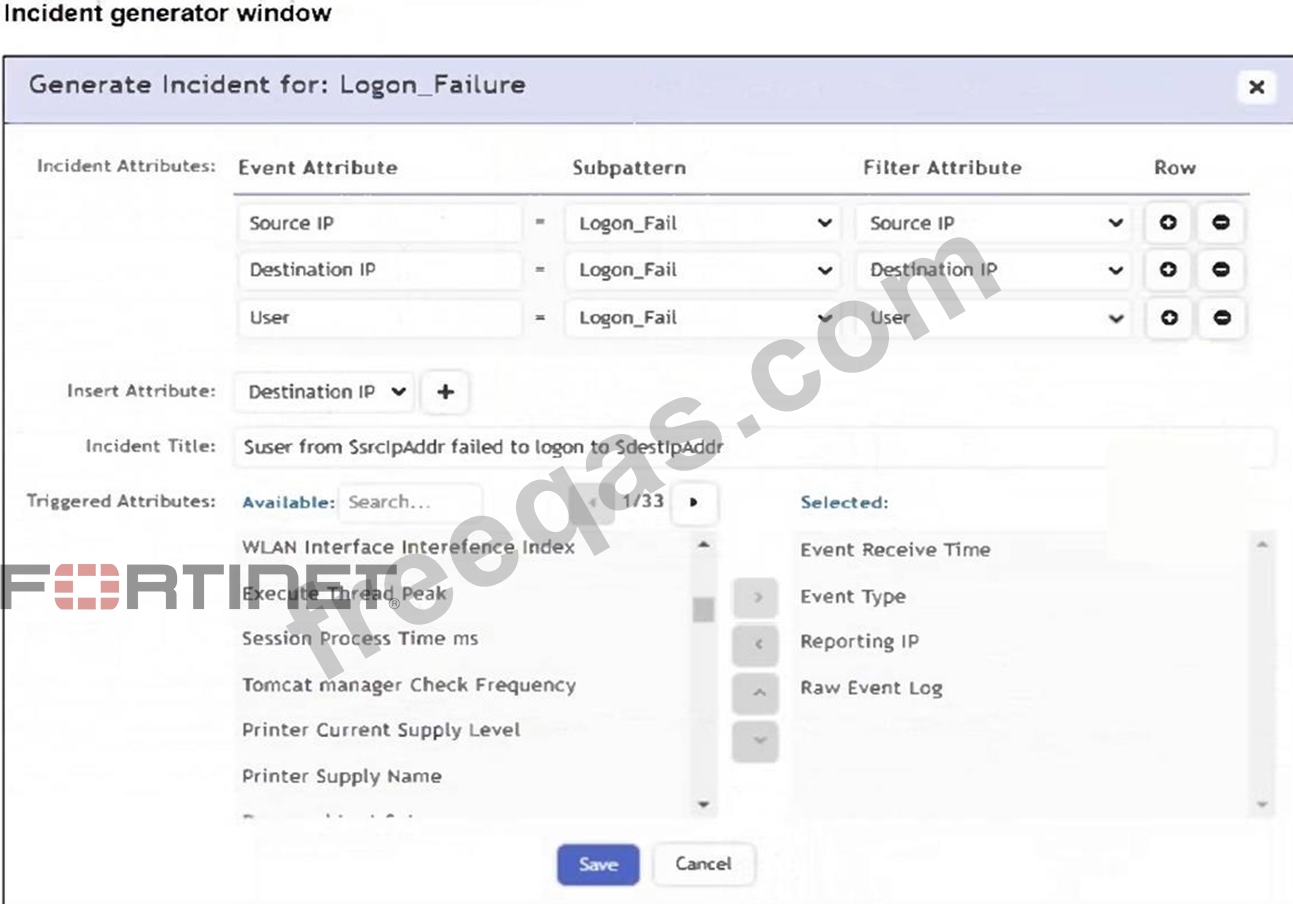
Refer to the exhibit.

An analyst is trying to generate an incident with a title that includes the Source IP, Destination IP, User, and Destination Host Name. They are unable to add a Destination Host Name as an incident attribute.
What must be changed to allow the analyst to select Destination Host Name as an attribute?

Correct Answer: A
For an attribute like Destination Host Name to be used in the incident title, it must first be included in the Triggered Attributes list. Only attributes listed there are available for substitution in the title template (e.g., $destIpAddr, $srcIpAddr).
insert code

Question 13

What can you use to send data to FortiSIEM for user and entity behavior analytics (UEBA)?

Correct Answer: A
The FortiSIEM agent can be used to send detailed endpoint data such as user activity and process behavior to FortiSIEM, which is essential for performing User and Entity Behavior Analytics (UEBA).
insert code

Question 14

Which statement about thresholds is true?

Correct Answer: A
insert code

Question 15

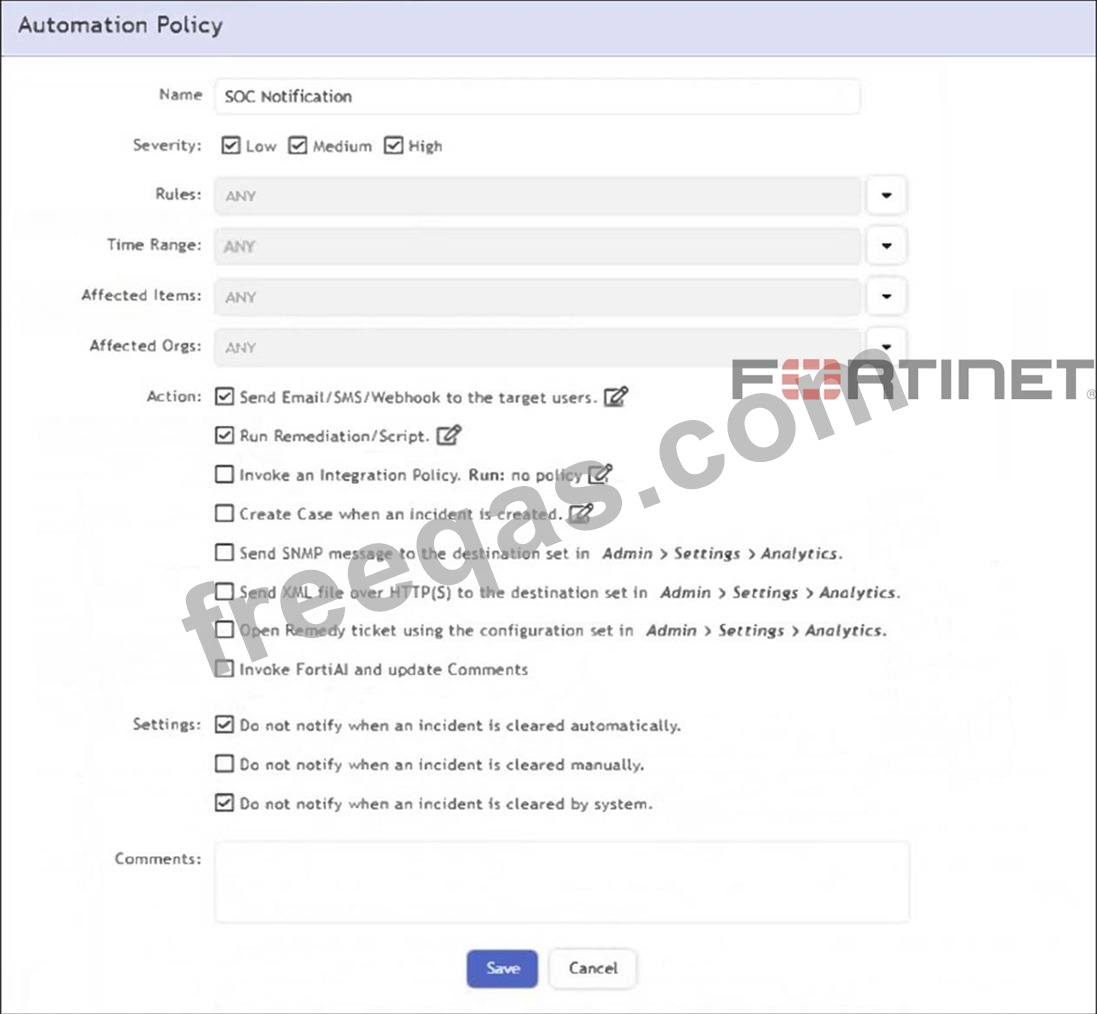
Refer to the exhibit.

What happens when an analyst clears an incident generated by a rule containing the automation policy shown in the exhibit?

Correct Answer: A
The automation policy has the option "Do not notify when an incident is cleared manually" enabled. Therefore, when an analyst manually clears an incident, no notification or automation action is triggered.
insert code
  • «
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • 7
  • 8
  • »
[×]

Download PDF File

Enter your email address to download Fortinet.FCP_FSM_AN-7.2.v2026-06-02.q31 Dumps

Email:

FreeQAs

Our website provides the Largest and the most Latest vendors Certification Exam materials around the world.

Using dumps we provide to Pass the Exam, we has the Valid Dumps with passing guranteed just which you need.

  • DMCA
  • About
  • Contact Us
  • Privacy Policy
  • Terms & Conditions
©2026 FreeQAs

www.freeqas.com materials do not contain actual questions and answers from Cisco's certification exams.