Your company has a Microsoft 365 E5 subscription. The company plans to deploy 45 mobile self-service kiosks that will run Windows 10. You need to provide recommendations to secure the kiosks. The solution must meet the following requirements: * Ensure that only authorized applications can run on the kiosks. * Regularly harden the kiosks against new threats. Which two actions should you include in the recommendations? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
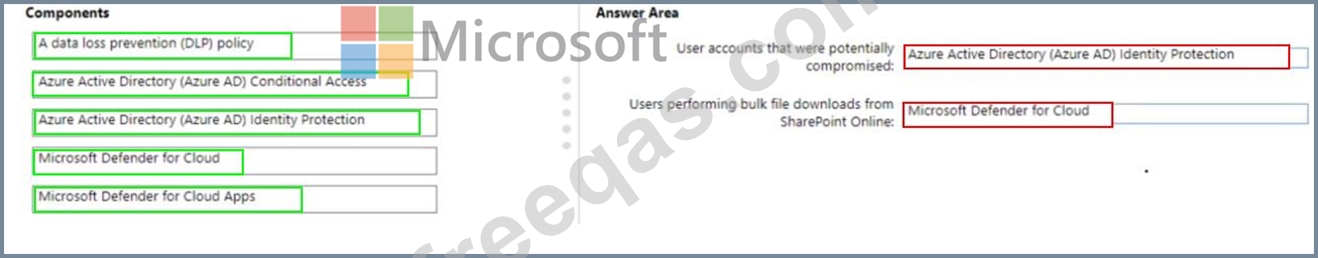
You have a Microsoft 365 subscription You need to recommend a security solution to monitor the following activities: * User accounts that were potentially compromised * Users performing bulk file downloads from Microsoft SharePoint Online What should you include in the recommendation for each activity? To answer, drag the appropriate components to the correct activities. Each component may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content. NOTE: Each Correct selection is worth one Point.
Correct Answer:
Question 43
You are designing a security strategy for providing access to Azure App Service web apps through an Azure Front Door instance. You need to recommend a solution to ensure that the web apps only allow access through the Front Door instance. Solution: You recommend access restrictions to allow traffic from the backend IP address of the Front Door instance. Does this meet the goal?
Correct Answer: B
Topic 1, Litware, inc. Case Study 2 Overview Litware, inc. is a financial services company that has main offices in New York and San Francisco. litware has 30 branch offices and remote employees across the United States. The remote employees connect to the main offices by using a VPN. Litware has grown significantly during the last two years due to mergers and acquisitions. The acquisitions include several companies based in France. Existing Environment Litware has an Azure Active Directory (Azure AD) tenant that syncs with an Active Directory Domain Services (AD D%) forest named Utvvare.com and is linked to 20 Azure subscriptions. Azure AD Connect is used to implement pass-through authentication. Password hash synchronization is disabled, and password writeback is enabled. All Litware users have Microsoft 365 E5 licenses. The environment also includes several AD DS forests, Azure AD tenants, and hundreds of Azure subscriptions that belong to the subsidiaries of Litware. Planned Changes Litware plans to implement the following changes: * Create a management group hierarchy for each Azure AD tenant. * Design a landing zone strategy to refactor the existing Azure environment of Litware and deploy all future Azure workloads. * Implement Azure AD Application Proxy to provide secure access to internal applications that are currently accessed by using the VPN. Business Requirements Litware identifies the following business requirements: * Minimize any additional on-premises infrastructure. * Minimize the operational costs associated with administrative overhead. Hybrid Requirements Litware identifies the following hybrid cloud requirements: * Enable the management of on-premises resources from Azure, including the following: *Use Azure Policy for enforcement and compliance evaluation. * Provide change tracking and asset inventory. * Implement patch management. * Provide centralized, cross-tenant subscription management without the overhead of maintaining guest accounts. Microsoft Sentinel Requirements Litware plans to leverage the security information and event management (SIEM) and security orchestration automated response (SOAK) capabilities of Microsoft Sentinel. The company wants to centralize Security Operations Center (SOQ by using Microsoft Sentinel. Identity Requirements Litware identifies the following identity requirements: * Detect brute force attacks that directly target AD DS user accounts. * Implement leaked credential detection in the Azure AD tenant of Litware. * Prevent AD DS user accounts from being locked out by brute force attacks that target Azure AD user accounts. * Implement delegated management of users and groups in the Azure AD tenant of Litware, including support for. * The management of group properties, membership, and licensing The management of user properties, passwords, and licensing * The delegation of user management based on business units. Regulatory Compliance Requirements Litware identifies the following regulatory compliance requirements: * insure data residency compliance when collecting logs, telemetry, and data owned by each United States- and France-based subsidiary. * Leverage built-in Azure Policy definitions to evaluate regulatory compliance across the entire managed environment. * Use the principle of least privilege. Azure Landing Zone Requirements Litware identifies the following landing zone requirements: * Route all internet-bound traffic from landing zones through Azure Firewall in a dedicated Azure subscription. * Provide a secure score scoped to the landing zone. * Ensure that the Azure virtual machines in each landing zone communicate with Azure App Service web apps in the same zone over the Microsoft backbone network, rather than over public endpoints. * Minimize the possibility of data exfiltration. * Maximize network bandwidth. The landing zone architecture will include the dedicated subscription, which will serve as the hub for internet and hybrid connectivity. Each landing zone will have the following characteristics: * Be created in a dedicated subscription. * Use a DNS namespace of litware.com. Application Security Requirements Litware identifies the following application security requirements: * Identify internal applications that will support single sign-on (SSO) by using Azure AD Application Proxy. * Monitor and control access to Microsoft SharePoint Online and Exchange Online data in real time.
Question 44
You have a Microsoft 365 subscription and an Azure subscription. Microsoft 365 Defender and Microsoft Defender for Cloud are enabled. The Azure subscription contains 50 virtual machines. Each virtual machine runs different applications on Windows Server 2019. You need to recommend a solution to ensure that only authorized applications can run on the virtual machines. If an unauthorized application attempts to run or be installed, the application must be blocked automatically until an administrator authorizes the application. Which security control should you recommend?
Correct Answer: D
Adaptive application controls are an intelligent and automated solution for defining allowlists of known-safe applications for your machines. Often, organizations have collections of machines that routinely run the same processes. Microsoft Defender for Cloud uses machine learning to analyze the applications running on your machines and create a list of the known-safe software. Allowlists are based on your specific Azure workloads, and you can further customize the recommendations using the instructions below. When you've enabled and configured adaptive application controls, you'll get security alerts if any application runs other than the ones you've defined as safe. Reference: https://docs.microsoft.com/en-us/azure/defender-for-cloud/adaptive-application-controls https://docs.microsoft.com/en-us/mem/intune/apps/app-protection-policy https://docs.microsoft.com/en-us/defender-cloud-apps/cloud-discovery-anomaly-detection-policy https://docs.microsoft.com/en-us/security/benchmark/azure/overview
Question 45
You need to recommend a solution to scan the application code. The solution must meet the application development requirements. What should you include in the recommendation?