FreeQAs
 Request Exam  Contact
  • Home
  • View All Exams
  • New QA's
  • Upload
PRACTICE EXAMS:
  • Oracle
  • Fortinet
  • Juniper
  • Microsoft
  • Cisco
  • Citrix
  • CompTIA
  • VMware
  • ISC
  • SAP
  • EMC
  • PMI
  • HP
  • Salesforce
  • Other
  • Oracle
    Oracle
  • Fortinet
    Fortinet
  • Juniper
    Juniper
  • Microsoft
    Microsoft
  • Cisco
    Cisco
  • Citrix
    Citrix
  • CompTIA
    CompTIA
  • VMware
    VMware
  • ISC
    ISC
  • SAP
    SAP
  • EMC
    EMC
  • PMI
    PMI
  • HP
    HP
  • Salesforce
    Salesforce
  1. Home
  2. Fortinet Certification
  3. FCP_FGT_AD-7.6 Exam
  4. Fortinet.FCP_FGT_AD-7.6.v2026-08-15.q97 Dumps
  • «
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • 7
  • 8
  • 9
  • 10
  • …
  • »
  • »»
Download Now

Question 6

Refer to the exhibit, which shows an SD-WAN zone configuration on the FortiGate GUI.
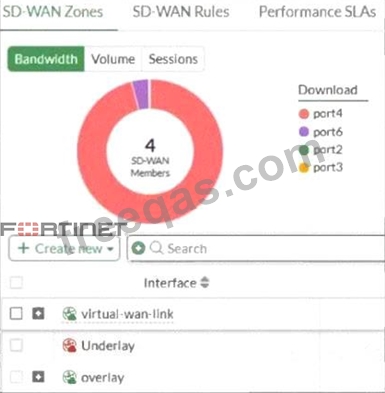
Based on the exhibit, which statement is true?

Correct Answer: A
The Underlay zone is the default SD-WAN zone, typically representing the physical interfaces in the SD- WAN configuration before overlay or virtual links are added.
insert code

Question 7

Which inspection mode does FortiGate use for application profiles if it is configured as a profile- based next-generation firewall (NGFW)?

Correct Answer: B
You can configure application control in proxy-based and flow-based firewall policies. However, because application control uses the IPS engine, which uses flow-based inspection, the INSPECTION is always flow-based.
insert code

Question 8

Refer to the exhibit. Why did the FortiGate device drop the packet?

Correct Answer: B
The packet trace shows policy-0 is matched, act-drop and Denied by forward policy check (policy
0). This means the packet matched an explicitly configured firewall policy (policy ID 0 in this case) whose action is set to DENY, and the traffic was dropped accordingly.
insert code

Question 9

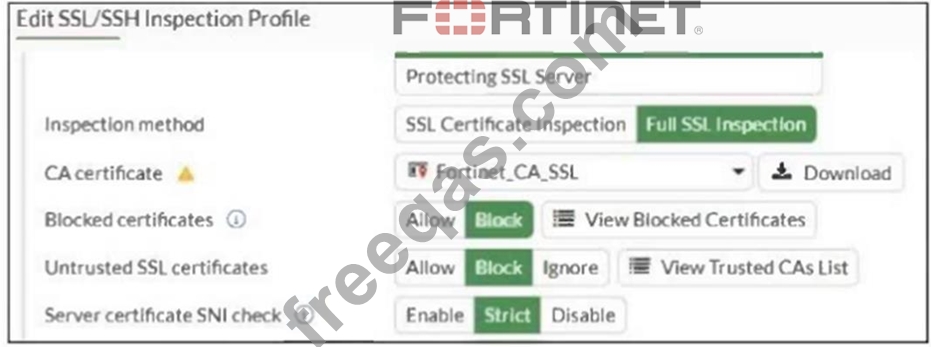
Refer to the exhibit. What would be the impact of these settings on the Server certificate SNI check configuration on FortiGate?
Correct Answer: C
SNI-server-cert-check
Enable: Check the SNI in the client hello message with the CN or SAN fields in the returned server certificate. If mismatched, use the CN in the server certificate to do URL filtering.
Strict: Check the SNI in the client hello message with the CN or SAN fields in the returned server certificate. If mismatched, close the connection.
Disable: Do not check the SNI in the client hello message with the CN or SAN fields in the returned server certificate.
insert code

Question 10

An administrator configures FortiGuard servers as DNS servers on FortiGate using default settings.
What is true about the DNS connection to a FortiGuard server?

Correct Answer: A
insert code
  • «
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • 7
  • 8
  • 9
  • 10
  • …
  • »
  • »»
[×]

Download PDF File

Enter your email address to download Fortinet.FCP_FGT_AD-7.6.v2026-08-15.q97 Dumps

Email:

FreeQAs

Our website provides the Largest and the most Latest vendors Certification Exam materials around the world.

Using dumps we provide to Pass the Exam, we has the Valid Dumps with passing guranteed just which you need.

  • DMCA
  • About
  • Contact Us
  • Privacy Policy
  • Terms & Conditions
©2026 FreeQAs

www.freeqas.com materials do not contain actual questions and answers from Cisco's certification exams.
