FreeQAs
 Request Exam  Contact
  • Home
  • View All Exams
  • New QA's
  • Upload
PRACTICE EXAMS:
  • Oracle
  • Fortinet
  • Juniper
  • Microsoft
  • Cisco
  • Citrix
  • CompTIA
  • VMware
  • ISC
  • SAP
  • EMC
  • PMI
  • HP
  • Salesforce
  • Other
  • Oracle
    Oracle
  • Fortinet
    Fortinet
  • Juniper
    Juniper
  • Microsoft
    Microsoft
  • Cisco
    Cisco
  • Citrix
    Citrix
  • CompTIA
    CompTIA
  • VMware
    VMware
  • ISC
    ISC
  • SAP
    SAP
  • EMC
    EMC
  • PMI
    PMI
  • HP
    HP
  • Salesforce
    Salesforce
  1. Home
  2. Fortinet Certification
  3. FCP_FGT_AD-7.6 Exam
  4. Fortinet.FCP_FGT_AD-7.6.v2026-08-15.q97 Dumps
  • ««
  • «
  • …
  • 4
  • 5
  • 6
  • 7
  • 8
  • 9
  • 10
  • 11
  • 12
  • 13
  • …
  • »
  • »»
Download Now

Question 36

You have configured an application control profile, set peer-to-peer traffic to Block under the Categories tab, and applied it to the firewall policy. However, your peer-to-peer traffic on known ports is passing through the FortiGate without being blocked.
What FortiGate settings should you check to resolve this issue?

Correct Answer: C
Network Protocol Enforcement settings control how FortiGate inspects and enforces protocols on traffic, including peer-to-peer applications on known ports. If not properly enabled, peer-to-peer traffic may bypass blocking despite the application control profile.
insert code

Question 37

Refer to the exhibit, which contains a RADIUS server configuration.
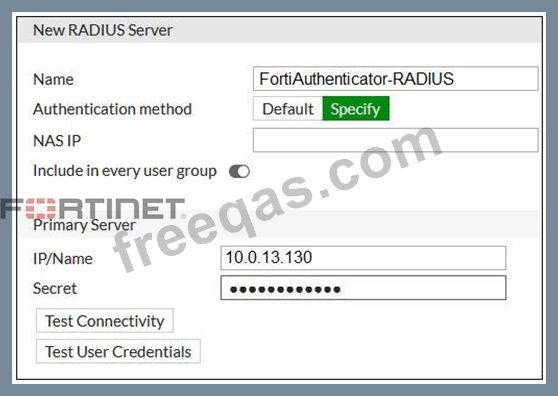
An administrator added a configuration for a new RADIUS server. While configuring, the administrator enabled Include in every user group.
What is the impact of enabling Include in every user group in a RADIUS configuration?

Correct Answer: A
The Include in every User Group optionadds the RADIUS server and all userswho can authenticate against it, to every user group created on FortiGate.
insert code

Question 38

Refer to the exhibit. The administrator configured SD-WAN rules and set the FortiGate traffic log page to display SD-WAN-specific columns: SD-WAN Quality and SD- WAN Rule Name.
FortiGate allows the traffic according to policy ID 1 placed at the top. This is the policy that allows SD-WAN traffic. Despite these settings, the traffic logs do not show the name of the SD-WAN rule used to steer those traffic flows.
What could be the reason?

Correct Answer: C
Note that the ImplicitSD-WAN rule name does not appear in the SD-WAN Rule Name column.
When the traffic is steered according to this rule, the field remains empty.
insert code

Question 39

Which statement is a characteristic of automation stitches?

Correct Answer: C
The stitch Action execution can be set to either Sequential or Parallel. In sequential execution, actions will execute one after another with a delay (if specified). If one action fails, then the action chain stops. This is the default setting. In parallel execution, all actions will execute immediately when the stitch is triggered.
insert code

Question 40

When FortiGate performs SSL/SSH full inspection, you can decide how it should react when it detects an invalid certificate.
Which three actions are valid actions that FortiGate can perform when it detects an invalid certificate?
(Choose three.)

Correct Answer: B,C,D
insert code
  • ««
  • «
  • …
  • 4
  • 5
  • 6
  • 7
  • 8
  • 9
  • 10
  • 11
  • 12
  • 13
  • …
  • »
  • »»
[×]

Download PDF File

Enter your email address to download Fortinet.FCP_FGT_AD-7.6.v2026-08-15.q97 Dumps

Email:

FreeQAs

Our website provides the Largest and the most Latest vendors Certification Exam materials around the world.

Using dumps we provide to Pass the Exam, we has the Valid Dumps with passing guranteed just which you need.

  • DMCA
  • About
  • Contact Us
  • Privacy Policy
  • Terms & Conditions
©2026 FreeQAs

www.freeqas.com materials do not contain actual questions and answers from Cisco's certification exams.
