FreeQAs
 Request Exam  Contact
  • Home
  • View All Exams
  • New QA's
  • Upload
PRACTICE EXAMS:
  • Oracle
  • Fortinet
  • Juniper
  • Microsoft
  • Cisco
  • Citrix
  • CompTIA
  • VMware
  • ISC
  • SAP
  • EMC
  • PMI
  • HP
  • Salesforce
  • Other
  • Oracle
    Oracle
  • Fortinet
    Fortinet
  • Juniper
    Juniper
  • Microsoft
    Microsoft
  • Cisco
    Cisco
  • Citrix
    Citrix
  • CompTIA
    CompTIA
  • VMware
    VMware
  • ISC
    ISC
  • SAP
    SAP
  • EMC
    EMC
  • PMI
    PMI
  • HP
    HP
  • Salesforce
    Salesforce
  1. Home
  2. Fortinet Certification
  3. FCP_FGT_AD-7.6 Exam
  4. Fortinet.FCP_FGT_AD-7.6.v2026-08-15.q97 Dumps
  • ««
  • «
  • …
  • 7
  • 8
  • 9
  • 10
  • 11
  • 12
  • 13
  • 14
  • 15
  • 16
  • …
  • »
  • »»
Download Now

Question 51

An administrator wants to analyze and manage digital certificates to prevent browser warnings when users connect to the SSL VPN portal.
Which two statements describe how to correctly do this? (Choose two.)

Correct Answer: C,D
Using a publicly trusted certificate from a known CA prevents browser warnings without additional user action.
Importing the FortiGate self-signed certificate into users' browsers as trusted eliminates warnings caused by untrusted certificates.
insert code

Question 52

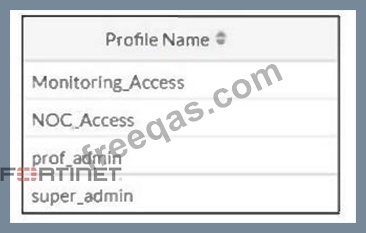
Refer to the exhibit. The NOC team connects to the FortiGate GUI with the NOC_Access admin profile. They request that their GUI sessions do not disconnect too early during inactivity. What must the administrator configure to answer this specific request from the NOC team?
Correct Answer: D
The admintimeout setting in the admin access profile controls the inactivity timeout for GUI sessions. Increasing this value will extend the session duration before automatic disconnection.
insert code

Question 53

A FortiGate firewall policy is configured with active authentication, however, the user cannot authenticate when accessing a website.
Which protocol must FortiGate allow even though the user cannot authenticate?

Correct Answer: A
DNS traffic must be allowed so the user can resolve domain names and reach the authentication server or web resources, even if authentication initially fails.
insert code

Question 54

Refer to the exhibits. The exhibits show the system performance output and default configuration of high memory usage thresholds on a FortiGate device.


Based on the system performance output, what are the two possible outcomes? (Choose two.)

Correct Answer: A,C
insert code

Question 55

Refer to the exhibit. Why did the FortiGate device drop the packet?

Correct Answer: A
In FortiGate, policy ID 0 is the implicit deny policy, a hidden, automatically added rule at the end of the security policy list that blocks any traffic not explicitly permitted by preceding user- configured policies.
insert code
  • ««
  • «
  • …
  • 7
  • 8
  • 9
  • 10
  • 11
  • 12
  • 13
  • 14
  • 15
  • 16
  • …
  • »
  • »»
[×]

Download PDF File

Enter your email address to download Fortinet.FCP_FGT_AD-7.6.v2026-08-15.q97 Dumps

Email:

FreeQAs

Our website provides the Largest and the most Latest vendors Certification Exam materials around the world.

Using dumps we provide to Pass the Exam, we has the Valid Dumps with passing guranteed just which you need.

  • DMCA
  • About
  • Contact Us
  • Privacy Policy
  • Terms & Conditions
©2026 FreeQAs

www.freeqas.com materials do not contain actual questions and answers from Cisco's certification exams.
