A company has Aruba APs that are controlled by Central and that implement WIDS. When you check WIDS events, you see a "detect valid SSID misuse" event. What can you interpret from this event, and what steps should you take?
A company wants to implement Virtual Network based Tunneling (VNBT) on a particular group of users and assign those users to an overlay network with VNI
3000.
Assume that an AOS-CX switch is already set up to:
. Implement 802.1X to HPE Aruba Networking ClearPass Policy Manager (CPPM)
. Participate in an EVPN VXLAN solution that includes VNI 3000
Which setting should you configure in the users' AOS-CX role to apply VNBT to them when they connect?
A company has several use cases for using its AOS-CX switches' HPE Aruba Networking Network Analytics Engine (NAE).
What is one guideline to keep in mind as you plan?
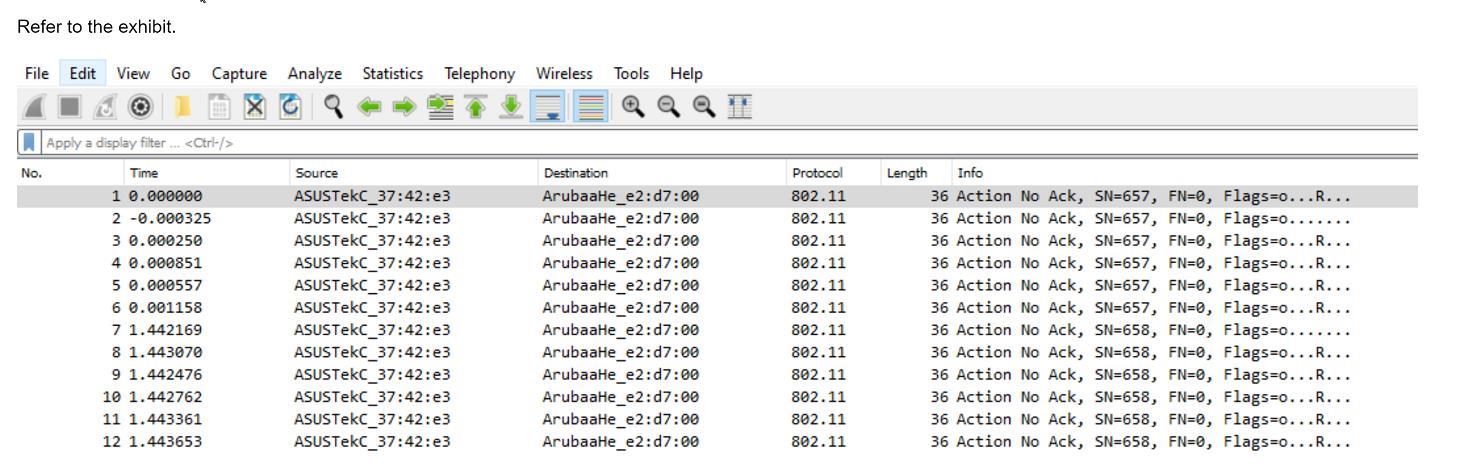
You have downloaded a packet capture that you generated on HPE Aruba Networking Central. When you open the capture in Wireshark, you see the output shown in the exhibit.
What should you do in Wireshark so that you can better interpret the packets?
A port-access role for AOS-CX switches has this policy applied to it:
plaintext
Copy code
port-access policy mypolicy
10 class ip zoneC action drop
20 class ip zoneA action drop
100 class ip zoneB
The classes have this configuration:
plaintext
Copy code
class ip zoneC
10 match tcp 10.2.0.0/16 eq https
class ip zoneA
10 match ip any 10.1.0.0/16
class ip zoneB
10 match ip any 10.0.0.0/8
The company wants to permit clients in this role to access 10.2.12.0/24 with HTTPS. What should you do?

