FreeQAs
 Request Exam  Contact
  • Home
  • View All Exams
  • New QA's
  • Upload
PRACTICE EXAMS:
  • Oracle
  • Fortinet
  • Juniper
  • Microsoft
  • Cisco
  • Citrix
  • CompTIA
  • VMware
  • ISC
  • SAP
  • EMC
  • PMI
  • HP
  • Salesforce
  • Other
  • Oracle
    Oracle
  • Fortinet
    Fortinet
  • Juniper
    Juniper
  • Microsoft
    Microsoft
  • Cisco
    Cisco
  • Citrix
    Citrix
  • CompTIA
    CompTIA
  • VMware
    VMware
  • ISC
    ISC
  • SAP
    SAP
  • EMC
    EMC
  • PMI
    PMI
  • HP
    HP
  • Salesforce
    Salesforce
  1. Home
  2. Microsoft Certification
  3. AZ-400 Exam
  4. Microsoft.AZ-400.v2025-02-10.q279 Dumps
  • ««
  • «
  • …
  • 41
  • 42
  • 43
  • 44
  • 45
  • 46
  • 47
  • 48
  • 49
  • 50
  • …
  • »
  • »»
Download Now

Question 221

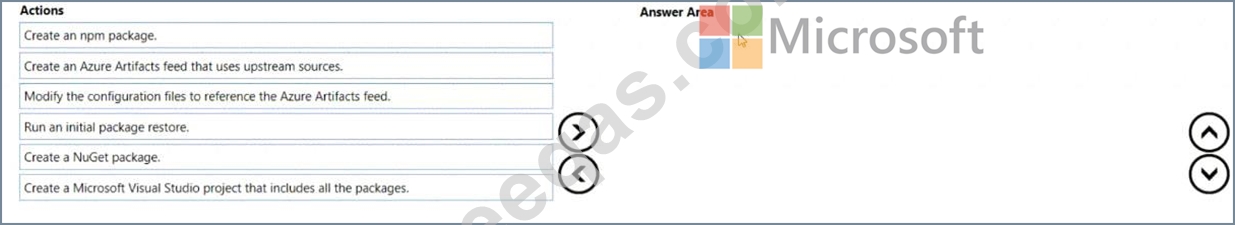
You have a project in Azure DevOps that uses packages from multiple public feeds. Some of the feeds are unreliable.
You need to consolidate the packages into a single feed.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Correct Answer:

Explanation

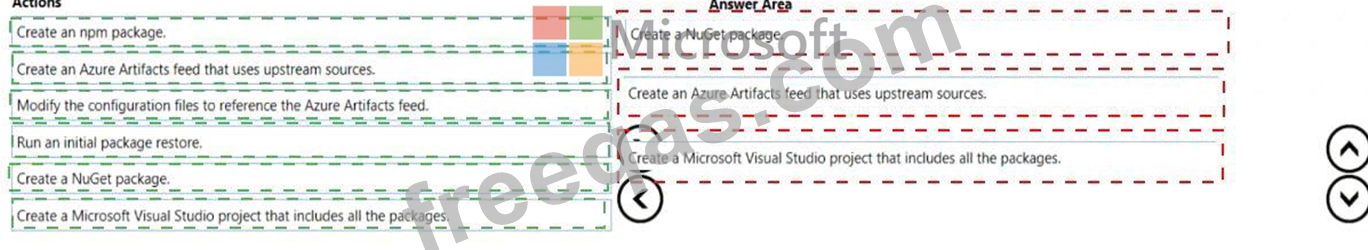
Step 1: Create a NuGet package.
NuGet and Maven are public package managers that support multiple feeds.
Step 2: Create an Azure Artifacts feed that uses upstream sources
If you want to use packages from multiple feeds, use upstream sources to bring packages from multiple feeds together into a single feed.
Step 3: Create a Micrtosoft Visual Studio project that includes all the packages Consume NuGet packages from upstream sources: Now you can open Visual Studio and install packages from the upstream sources you just configured.
Reference:
https://docs.microsoft.com/en-us/azure/devops/artifacts/how-to/set-up-upstream-sources
insert code

Question 222

You use Azure Pipelines lo manage the build and deployment of apps.
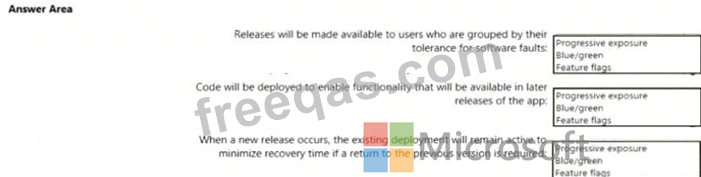
You are planning the release strategies for a new app. You need to choose strategies for the following scenarios:
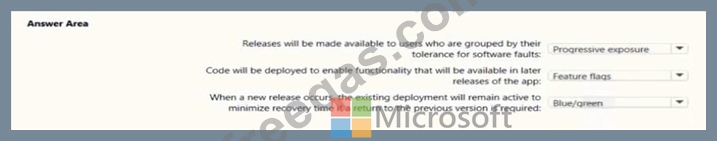
* Releases will be made available to users who are grouped by their tolerance for software faults.
* Code will be deployed to enable functionality that will be available in later releases of the app.
* When a new release occurs, the existing deployment will remain active to minimize recovery time if a return to the previous version is required.
Correct Answer:

Explanation

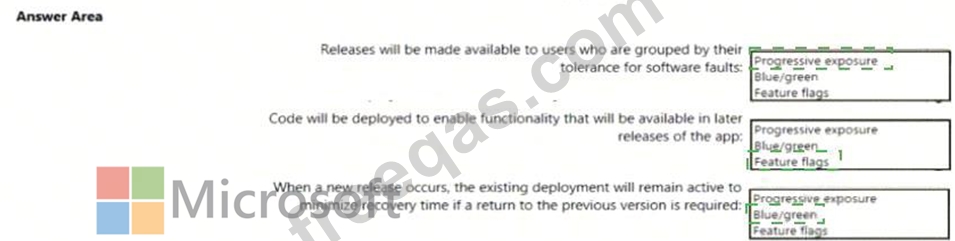
Box 1: Progressive exposure
Continuous Delivery may sequence multiple deployment "rings" for progressive exposure (also known as
"controlling the blast radius"). Progressive exposure groups users who get to try new releases to monitor their experience in "rings." The first deployment ring is often a "canary" used to test new versions in production before a broader rollout. CD automates deployment from one ring to the next and may optionally depend on an approval step, in which a decision maker signs off on the changes electronically. CD may create an auditable record of the approval in order to satisfy regulatory procedures or other control objectives.

Box 2: Feature flags
Feature flags support a customer-first DevOps mindset, to enable (expose) and disable (hide) features in a solution, even before they are complete and ready for release.
Box 3: Blue/green
Blue/green deployments which means that instead of replacing the previous version (here we refer to this version as blue), we bring up the new version (here referred to as the green version) next to the existing version, but not expose it to the actual users right away. On the condition of having successfully validated that the green version works correctly, we will promote this version to the public version by changing the routing configuration without downtime. If something is wrong with the green version we can revert back without users every noticing interruptions.
Reference:
https://docs.microsoft.com/en-us/azure/devops/learn/what-is-continuous-delivery
https://docs.microsoft.com/en-us/azure/devops/migrate/phase-features-with-feature-flags
https://medium.com/@denniszielke/continuous-kubernetes-blue-green-deployments-on-azure-using-nginx-appga
insert code

Question 223

Your company has an on-premises Bitbucket Server that is used for Git-based source control. The server is protected by a firewall that blocks inbound Internet traffic.
You plan to use Azure DevOps to manage the build and release processes
Which two components are required to integrate Azure DevOps and Bitbucket?
Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one port.

Correct Answer: A,D
When a pipeline uses a remote, 3rd-party repository host such as Bitbucket Cloud, the repository is configured with webooks that notify Azure Pipelines Server or TFS when code has changed and a build should be triggered. Since on-premises installations are normally protected behind a firewall, 3rd-party webhooks are unable to reach the on-premises server. As a workaround, you can use the External Git repository type which uses polling instead of webhooks to trigger a build when code has changed.
References: https://docs.microsoft.com/en-us/azure/devops/pipelines/repos/pipeline-options-for
insert code

Question 224

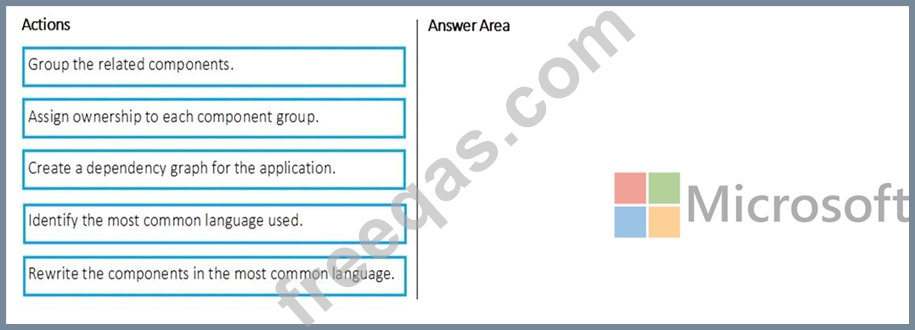
You need to find and isolate shared code. The shared code will be maintained in a series of packages.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Correct Answer:

Explanation:

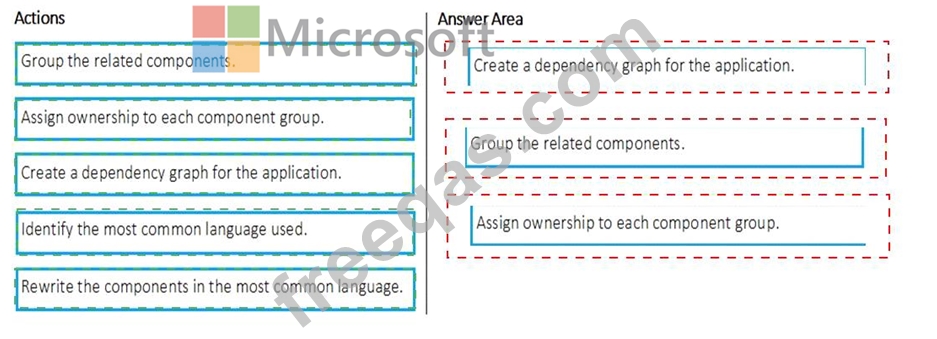
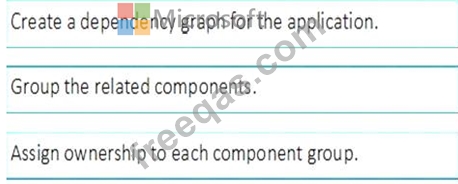
Step 1: Create a dependency graph for the application
By linking work items and other objects, you can track related work, dependencies, and changes made over time. All links are defined with a specific link type. For example, you can use Parent/Child links to link work items to support a hierarchical tree structure. Whereas, the Commit and Branch link types support links between work items and commits and branches, respectively.
Step 2: Group the related components.
Packages enable you to share code across your organization: you can compose a large product, develop multiple products based on a common shared framework, or create and share reusable components and libraries.
Step 3: Assign ownership to each component graph
References:
https://docs.microsoft.com/en-us/azure/devops/boards/queries/link-work-items-support-traceability?view=azure-
https://docs.microsoft.com/en-us/visualstudio/releasenotes/tfs2017-relnotes
insert code

Question 225

You are designing the security validation strategy for a project in Azure DevOps.
You need to identify package dependencies that have known security issues and can be resolved by an update.
What should you use?


Correct Answer: A
Incorrect Answers:
B: Jenkins is a popular open-source automation server used to set up continuous integration and delivery (CI/ CD) for your software projects.
D: SonarQube is a set of static analyzers that can be used to identify areas of improvement in your code. It allows you to analyze the technical debt in your project and keep track of it in the future.
Reference:
https://octopus.com/docs/packaging-applications
insert code
  • ««
  • «
  • …
  • 41
  • 42
  • 43
  • 44
  • 45
  • 46
  • 47
  • 48
  • 49
  • 50
  • …
  • »
  • »»
[×]

Download PDF File

Enter your email address to download Microsoft.AZ-400.v2025-02-10.q279 Dumps

Email:

FreeQAs

Our website provides the Largest and the most Latest vendors Certification Exam materials around the world.

Using dumps we provide to Pass the Exam, we has the Valid Dumps with passing guranteed just which you need.

  • DMCA
  • About
  • Contact Us
  • Privacy Policy
  • Terms & Conditions
©2026 FreeQAs

www.freeqas.com materials do not contain actual questions and answers from Cisco's certification exams.