FreeQAs
 Request Exam  Contact
  • Home
  • View All Exams
  • New QA's
  • Upload
PRACTICE EXAMS:
  • Oracle
  • Fortinet
  • Juniper
  • Microsoft
  • Cisco
  • Citrix
  • CompTIA
  • VMware
  • ISC
  • SAP
  • EMC
  • PMI
  • HP
  • Salesforce
  • Other
  • Oracle
    Oracle
  • Fortinet
    Fortinet
  • Juniper
    Juniper
  • Microsoft
    Microsoft
  • Cisco
    Cisco
  • Citrix
    Citrix
  • CompTIA
    CompTIA
  • VMware
    VMware
  • ISC
    ISC
  • SAP
    SAP
  • EMC
    EMC
  • PMI
    PMI
  • HP
    HP
  • Salesforce
    Salesforce
  1. Home
  2. Fortinet Certification
  3. FCP_FGT_AD-7.6 Exam
  4. Fortinet.FCP_FGT_AD-7.6.v2026-08-15.q97 Dumps
  • ««
  • «
  • …
  • 12
  • 13
  • 14
  • 15
  • 16
  • 17
  • 18
  • 19
  • 20
  • 21
  • »
Download Now

Question 81

A network administrator enabled antivirus and selected an SSL inspection profile on a firewall policy. When downloading an EICAR test file through HTTP, FortiGate detects the virus and blocks the file. When downloading the same file through HTTPS, FortiGate does not detect the virus and does not block the file, allowing it to be downloaded.
The administrator confirms that the traffic matches the configured firewall policy. What are two reasons for the failed virus detection by FortiGate? (Choose two.)

Correct Answer: A,B
Certificate inspection is not deep ssl inspection hence no inspection of the packet would happen since it is encrypted.
If the https site is in exampted list then yes it is a valid reason.
insert code

Question 82

Which three statements about SD-WAN performance SLAs are true? (Choose three.)

Correct Answer: A,B,E
SD-WAN SLAs monitor metrics like packet loss and jitter to evaluate link performance.
SLA measurements can be performed using active probing or passive monitoring.
Administrators can configure all SLA target parameters to define performance criteria.
insert code

Question 83

Which three pieces of information does FortiGate use to identify the hostname of the SSL server when SSL certificate inspection is enabled? (Choose three.)

Correct Answer: B,C,D
When using SSL certificate inspection, FortiGate is not decrypting the traffic. During the exchange of hello messages at the beginning of an SSL handshake, FortiGate parses the server name indication (SNI) from client Hello, which is an extension of the TLS protocol. The SNI tells FortiGate the hostname of the SSL server, which is validated against the DNS name before receipt of the server certificate. If there is no SNI exchanged, then FortiGate identifies the server by the value in the server by the value in the Subject field or SAN (Subject Alternative Name) field in the server certificate.
insert code

Question 84

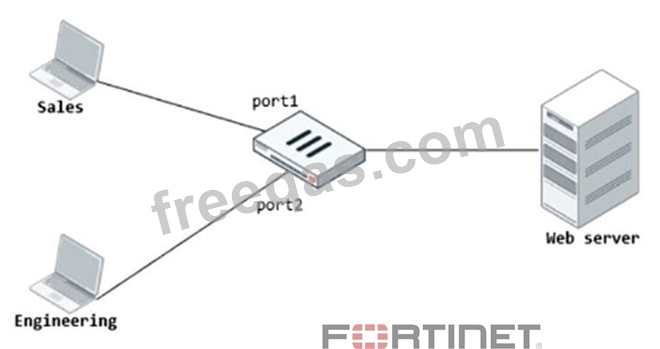
Refer to the exhibit.

FortiGate has two separate firewall policies for Sales and Engineering to access the same web server with the same security profiles.
Which action must the administrator perform to consolidate the two policies into one?

Correct Answer: A
To consolidate two firewall policies that use different incoming interfaces (port1 and port2) but have the same destination, services, and security profiles, the administrator should create an Interface Group that includes both port1 and port2.
This allows a single firewall policy to apply to traffic from both interfaces, simplifying management while maintaining consistent security enforcement.
insert code

Question 85

An administrator configured a FortiGate device to act as a collector for agentless polling mode.
What must the administrator add to the FortiGate device to retrieve AD user group information?

Correct Answer: B
In agentless polling mode, FortiGate directly queries Active Directory to obtain user and group information. To do this, the administrator must configure an LDAP server on the FortiGate, which allows it to retrieve user group membership details from AD.
insert code
  • ««
  • «
  • …
  • 12
  • 13
  • 14
  • 15
  • 16
  • 17
  • 18
  • 19
  • 20
  • 21
  • »
[×]

Download PDF File

Enter your email address to download Fortinet.FCP_FGT_AD-7.6.v2026-08-15.q97 Dumps

Email:

FreeQAs

Our website provides the Largest and the most Latest vendors Certification Exam materials around the world.

Using dumps we provide to Pass the Exam, we has the Valid Dumps with passing guranteed just which you need.

  • DMCA
  • About
  • Contact Us
  • Privacy Policy
  • Terms & Conditions
©2026 FreeQAs

www.freeqas.com materials do not contain actual questions and answers from Cisco's certification exams.