Your company is developing a serverless application in Azure that will have the architecture shown in the following exhibit.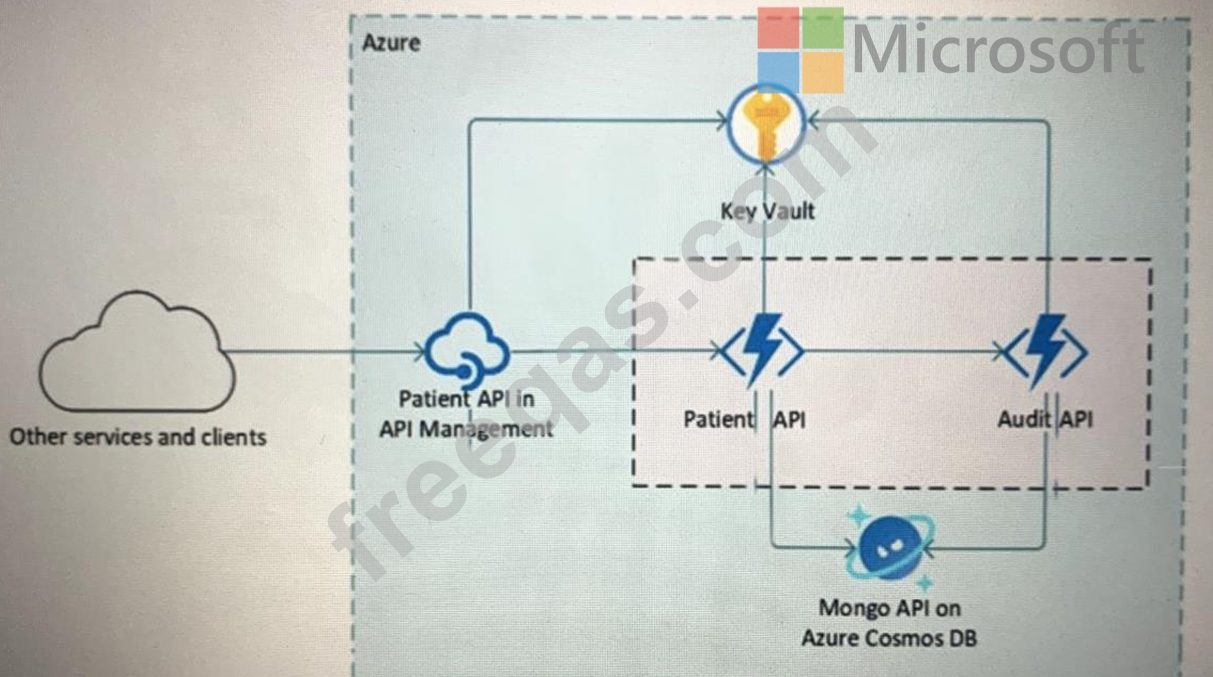
You need to recommend a solution to isolate the compute components on an Azure virtual network. What should you include in the recommendation?
You need to design a strategy for securing the SharePoint Online and Exchange Online dat
a. The solution must meet the application security requirements.
Which two services should you leverage in the strategy? Each correct answer presents part of the solution. NOTE; Each correct selection is worth one point.
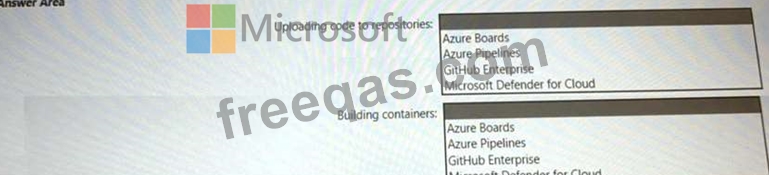
Your company has an Azure App Service plan that is used to deploy containerized web apps. You are designing a secure DevOps strategy for deploying the web apps to the App Service plan. You need to recommend a strategy to integrate code scanning tools into a secure software development lifecycle. The code must be scanned during the following two phases:
Uploading the code to repositories Building containers
Where should you integrate code scanning for each phase? To answer, select the appropriate options in the answer area.
You have an on-premises app that processes Personally Identifiable Information (PII) and sends the data to Azure .
The app includes the following components:
* APIs that receive and send the PII
* A data ingestion pipeline that stores the PII in an Azure Data Lake Storage Gen2 account A compliance policy requires that all the PII data be encrypted by using encryption keys that are regularly rotated and stored in a central repository.
You need to recommend a solution that adhere to the compliance policy. The solution must minimize administrative effort.
Which two components should you include in the recommendation? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point
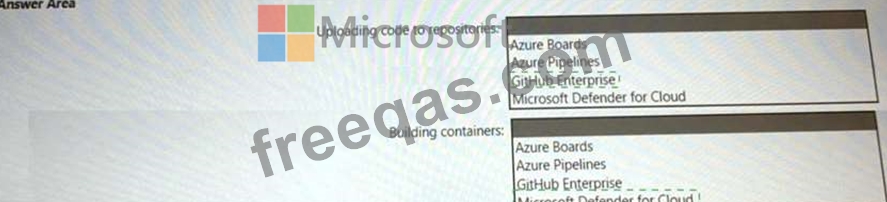
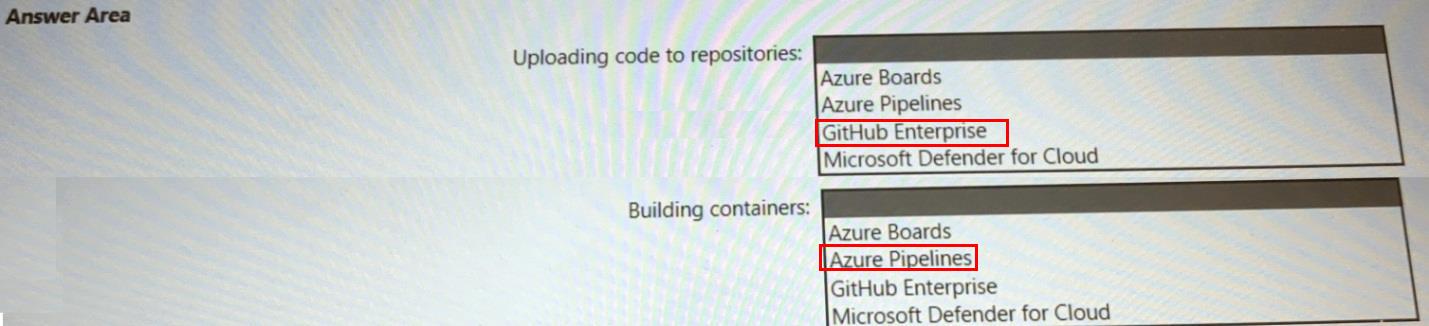
Your company has an Azure App Service plan that is used to deploy containerized web apps. You are designing a secure DevOps strategy for deploying the web apps to the App Service plan. You need to recommend a strategy to integrate code scanning tools into a secure software development lifecycle. The code must be scanned during the following two phases:
Uploading the code to repositories Building containers
Where should you integrate code scanning for each phase? To answer, select the appropriate options in the answer area.