You have an Azure subscription that contains a web app named App1. App1 uses a Microsoft Entra user account named SRV1 as a service account to authenticate to an Azure SQL database named DB1.
You discover that a developer accessed DB1 directly by using SRV1.
You need to recommend a secure authentication method that will prevent credential misuse outside of App1. The solution must minimize administrative effort.
What should you recommend?
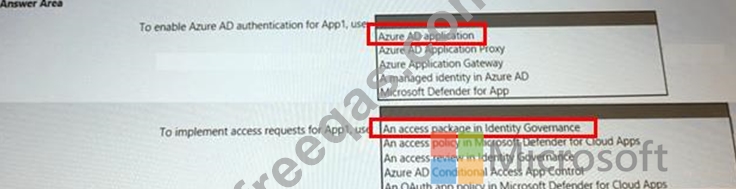
You are creating the security recommendations for an Azure App Service web app named App1.
App1 has the following specifications:
* Users will request access to App1 through the My Apps portal. A human resources manager will approve the requests.
* Users will authenticate by using Azure Active Directory (Azure AD) user accounts.
You need to recommend an access security architecture for App1.
What should you include in the recommendation? To answer, select the appropriate options in the answer are a. NOTE: Each correct selection is worth one point.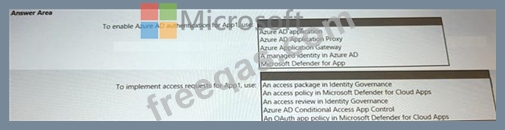
You have a Microsoft 365 E5 subscription and an Azure subscripts You need to evaluate the existing environment to increase the overall security posture for the following components:
* Windows 11 devices managed by Microsoft Intune
* Azure Storage accounts
* Azure virtual machines
What should you use to evaluate the components? To answer, select the appropriate options in the answer area.

You have an Azure subscription that contains 15 custom apps. The source files for the apps are stored in Git repositories. The apps are deployed by using Azure DevOps.
You need to recommend a DevSecOps solution to implement static application security testing (SAST) of the app code to identify hard-coded secrets.
What should you include in the recommendation?
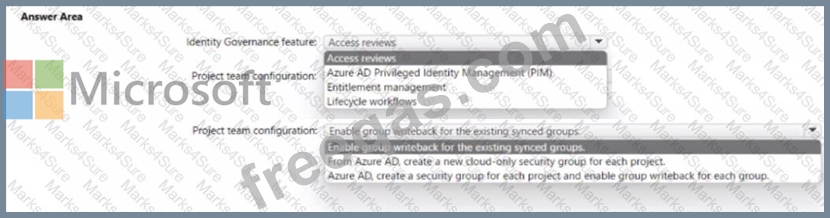
Your network contains an on-premises Active Directory Domain Services (AO DS) domain. The domain contains a server that runs Windows Server and hosts shared folders The domain syncs with Azure AD by using Azure AD Connect Azure AD Connect has group writeback enabled.
You have a Microsoft 365 subscription that uses Microsoft SharePoint Online.
You have multiple project teams. Each team has an AD DS group that syncs with Azure AD Each group has permissions to a unique SharePoint Online site and a Windows Server shared folder for its project. Users routinely move between project teams.
You need to recommend an Azure AD identity Governance solution that meets the following requirements:
* Project managers must verify that their project group contains only the current members of their project team
* The members of each project team must only have access to the resources of the project to which they are assigned
* Users must be removed from a project group automatically if the project manager has MOT verified the group s membership for 30 days.
* Administrative effort must be minimized.
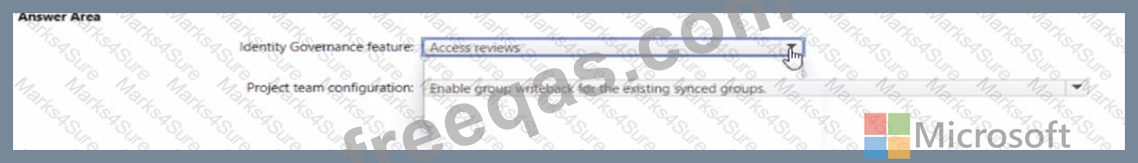
What should you include in the recommendation? To answer select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.