Your company has a Microsoft 365 subscription and uses Microsoft Defender for Identity. You are informed about incidents that relate to compromised identities.
You need to recommend a solution to expose several accounts for attackers to exploit. When the attackers attempt to exploit the accounts, an alert must be triggered. Which Defender for Identity feature should you include in the recommendation?
You are designing security for an Azure landing zone. Your company identifies the following compliance and privacy requirements:
* Encrypt cardholder data by using encryption keys managed by the company.
* Encrypt insurance claim files by using encryption keys hosted on-premises.
Which two configurations meet the compliance and privacy requirements? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
You have a Microsoft Entra tenant named contoso.com and use Microsoft Intune. Each user in contoso.com has a Microsoft Entra ID P1 license and a Windows 11 device that has the Global Secure Access client deployed.
You plan to deploy the following configuration of Microsoft Entra Internet Access:
* Enable a baseline profile.
* Create a security profile named Profile` that has a priority of 300 and contains a single web content filtering policy named WCFPolicy configure WCFPolicy1 as follows:
o Set Action to allow.
o Include a single rule that has a fully qualified domain name (FQDN) destination of '. adatum.com.
* Link Profile1 to a Conditional Access policy named CAPolicy1, apply CAPolicy1 to all users, and grant access unless a user's device is noncompliant You need to evaluate the impact of the planned deployment on traffic to the following resources:
* https://www.adatum.com:8433
* https://www.fabrikam.com
Which two traffic scenarios will occur? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point
Your company has an Azure App Service plan that is used to deploy containerized web apps. You are designing a secure DevOps strategy for deploying the web apps to the App Service plan. You need to recommend a strategy to integrate code scanning tools into a secure software development lifecycle. The code must be scanned during the following two phases:
Uploading the code to repositories Building containers
Where should you integrate code scanning for each phase? To answer, select the appropriate options in the answer area.

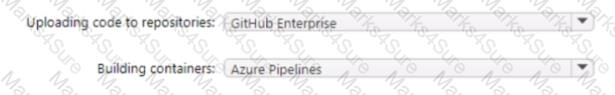
Hotspot Question
You have an Azure subscription that contains two virtual machines named VM1 and VM2 and an Azure App Service Standard app named App1. VM1 is used to upload data to App1. App1 stores data on VM2.
You need to secure connectivity between the virtual machines and App1. The solution must minimize the risk of data exfiltration.
What should you use to manage connectivity for App1? To answer, select the options in the answer area.
NOTE: Each correct answer is worth one point.


