You have a Microsoft 365 subscription.
You are designing a user access solution that follows the Zero Trust principles of the Microsoft Cybersecurity Reference Architectures (MCRA).
You need to recommend a solution that automatically restricts access to Microsoft Exchange Online, SharePoint Online, and Teams in near-real-time (NRT) in response to the following Azure AD events:
- A user account is disabled or deleted.
- The password of a user is changed or reset.
- All the refresh tokens for a user are revoked.
- Multi-factor authentication (MFA) is enabled for a user.
Which two features should you include in the recommendation? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
Your company has Microsoft 365 E5 licenses and Azure subscriptions.
The company plans to automatically label sensitive data stored in the following locations:
* Microsoft SharePoint Online
* Microsoft Exchange Online
* Microsoft Teams
You need to recommend a strategy to identify and protect sensitive data.
Which scope should you recommend for the sensitivity label policies? To answer, drag the appropriate scopes to the correct locations. Each scope may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.

You have an on-premises server named Server 1. Server1 is an FTP server that can be accessed by only the users at your company.
You have an Azure subscription.
You need to recommend a Zero Trust Network Access (ZTNA) solution to enforce Conditional Access policies when users access Server1 from the internet.
What should you include in the recommendation?
You receive a security alert in Microsoft Defender for Cloud as shown in the exhibit. (Click the Exhibit tab.)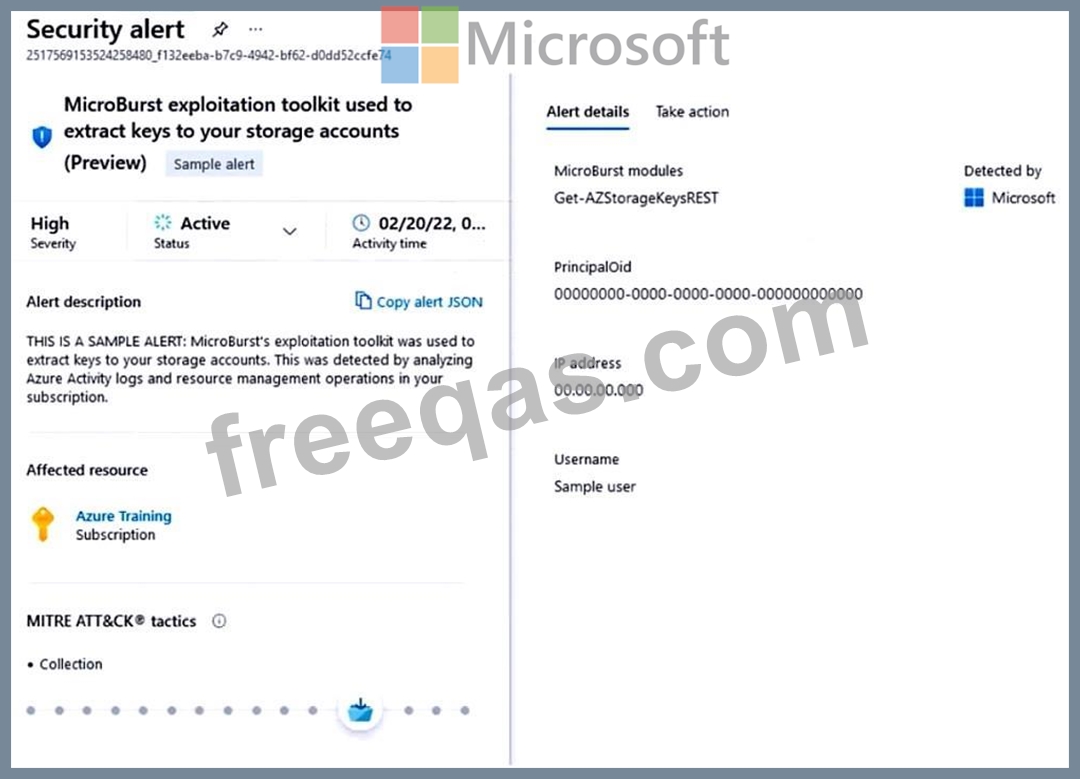
After remediating the threat which policy definition should you assign to prevent the threat from reoccurring?
You have an Azure subscription that has Microsoft Defender for Cloud enabled. You are evaluating the Azure Security Benchmark V3 report.
In the Secure management ports controls, you discover that you have 0 out of a potential 8 points. You need to recommend configurations to increase the score of the Secure management ports controls. Solution: You recommend enabling adaptive network hardening. Does this meet the goal?

