Hotspot Question
You have an Azure subscription that contains a Microsoft Sentinel workspace named MSW1.
MSW11 includes 50 scheduled analytics rules.
You need to design a security orchestration automated response (SOAR) solution by using Microsoft Sentinel playbooks. The solution must meet the following requirements:
- Ensure that expiration dates can be configured when a playbook runs.
- Minimize the administrative effort required to configure individual
analytics rules.
What should you use to invoke the playbooks, and which type of Microsoft Sentinel trigger should you use? To answer, select the options in the answer area.
NOTE: Each correct selection is worth one point.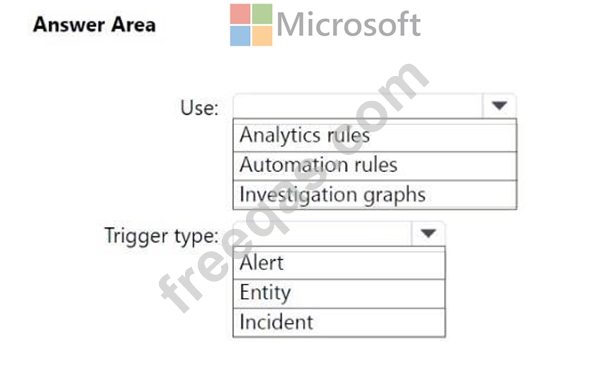

Azure subscription that uses Azure Storage.
The company plans to share specific blobs with vendors. You need to recommend a solution to provide the vendors with secure access to specific blobs without exposing the blobs publicly. The access must be t\me- Vim\ted. What should you include in the recommendation?
You have a Microsoft 365 subscription
You need to recommend a security solution to monitor the following activities:
* User accounts that were potentially compromised
* Users performing bulk file downloads from Microsoft SharePoint Online What should you include in the recommendation for each activity? To answer, drag the appropriate components to the correct activities. Each component may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each Correct selection is worth one Point.

Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have a Microsoft 365 subscription that uses Microsoft Defender XDR. The subscription contains 500 devices that are enrolled in Microsoft Intune. The subscription contains 500 users that connect to external software as a service (SaaS) apps by using the devices.
You need to implement a solution that meets the following requirements:
* Allows user access to SaaS apps that Microsoft has identified as low risk.
* Blocks user access to Saas apps that Microsoft has identified as high risk.
Solution: From Microsoft Defender for Cloud Apps, you configure a cloud discovery policy and unsanction risky apps.
Does this meet the goal?
You have a Microsoft 365 tenant.
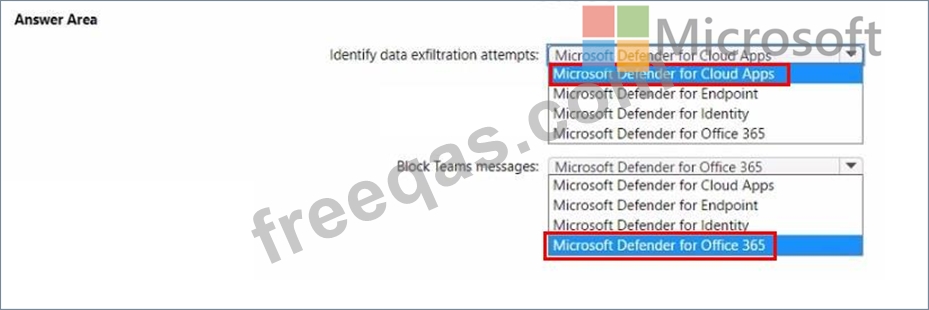
You need to recommend a Microsoft 365 Defender solution to enhance security for the tenant. The solution must meet the following requirements:
* Identify users that are downloading an unusually high number of files from Microsoft SharePoint Online sites and are possibly involved in a data exfiltration attempt.
* Block Microsoft Teams messages that contain potentially malicious content by using zero-hour auto purge (ZAP).
What should you recommend for each requirement? To answer, select the appropriate options in the answer are a. NOTE: Each correct selection is worth one point.