FreeQAs
 Request Exam  Contact
  • Home
  • View All Exams
  • New QA's
  • Upload
PRACTICE EXAMS:
  • Oracle
  • Fortinet
  • Juniper
  • Microsoft
  • Cisco
  • Citrix
  • CompTIA
  • VMware
  • ISC
  • SAP
  • EMC
  • PMI
  • HP
  • Salesforce
  • Other
  • Oracle
    Oracle
  • Fortinet
    Fortinet
  • Juniper
    Juniper
  • Microsoft
    Microsoft
  • Cisco
    Cisco
  • Citrix
    Citrix
  • CompTIA
    CompTIA
  • VMware
    VMware
  • ISC
    ISC
  • SAP
    SAP
  • EMC
    EMC
  • PMI
    PMI
  • HP
    HP
  • Salesforce
    Salesforce
  1. Home
  2. ECCouncil Certification
  3. 312-96 Exam
  4. ECCouncil.312-96.v2024-07-23.q33 Dumps
  • «
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • 7
  • 8
  • »
Download Now

Question 16

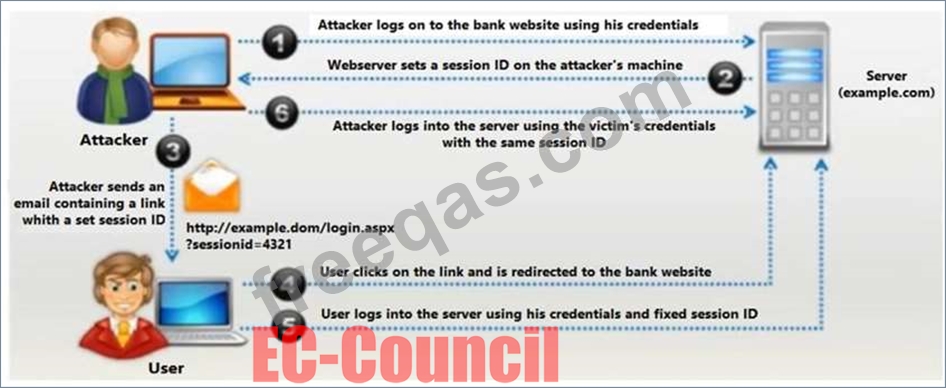
Identify the type of attack depicted in the figure below:

Correct Answer: D
insert code

Question 17

In which phase of secure development lifecycle the threat modeling is performed?

Correct Answer: D
insert code

Question 18

Which of the following can be derived from abuse cases to elicit security requirements for software system?

Correct Answer: A
Misuse cases are derived from abuse cases and are used to elicit security requirements for a software system.
They help in identifying and understanding how an application can be attacked or misused, which is essential for defining the security measures needed to protect the system. By analyzing misuse cases, developers and security engineers can anticipate potential threats and design the system to be resilient against them.
References: The concept of misuse cases is supported by various resources on application security and is aligned with the teachings of the EC-Council's Certified Application Security Engineer (CASE) JAVA program. The references from the web search results and the EC-Council's own documentation on the CASE JAVA certification emphasize the importance of understanding abuse cases to derive misuse cases for better security requirement elicitation123.
insert code

Question 19

Which of the following elements in web.xml file ensures that cookies will be transmitted over an encrypted channel?

Correct Answer: D
To ensure that cookies are transmitted securely over an encrypted channel, such as HTTPS, the web.xml file should include the secure attribute set to true within the cookie-config element of the session-config. This is not directly related to the connector element but rather to the session configuration for cookies.
Here's how it should be configured:
XML
<session-config>
<cookie-config>
<http-only>true</http-only>
<secure>true</secure>
</cookie-config>
</session-config>
AI-generated code. Review and use carefully. More info on FAQ.
This configuration ensures that cookies are only sent to the client when a secure channel is used.
References:The information is based on standard practices for securing cookies in Java web applications as per Servlet 3.0 specification and the OWASP guidelines. For more detailed information, you can refer to the EC-Council's Certified Application Security Engineer (CASE) JAVA documentation and study guides1234.
insert code

Question 20

Oliver is a web server admin and wants to configure the Tomcat server in such a way that it should not serve index pages in the absence of welcome files. Which of the following settings in CATALINA_HOME/conf/ in web.xml will solve his problem?


Correct Answer: C
insert code
  • «
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • 7
  • 8
  • »
[×]

Download PDF File

Enter your email address to download ECCouncil.312-96.v2024-07-23.q33 Dumps

Email:

FreeQAs

Our website provides the Largest and the most Latest vendors Certification Exam materials around the world.

Using dumps we provide to Pass the Exam, we has the Valid Dumps with passing guranteed just which you need.

  • DMCA
  • About
  • Contact Us
  • Privacy Policy
  • Terms & Conditions
©2026 FreeQAs

www.freeqas.com materials do not contain actual questions and answers from Cisco's certification exams.