FreeQAs
 Request Exam  Contact
  • Home
  • View All Exams
  • New QA's
  • Upload
PRACTICE EXAMS:
  • Oracle
  • Fortinet
  • Juniper
  • Microsoft
  • Cisco
  • Citrix
  • CompTIA
  • VMware
  • ISC
  • SAP
  • EMC
  • PMI
  • HP
  • Salesforce
  • Other
  • Oracle
    Oracle
  • Fortinet
    Fortinet
  • Juniper
    Juniper
  • Microsoft
    Microsoft
  • Cisco
    Cisco
  • Citrix
    Citrix
  • CompTIA
    CompTIA
  • VMware
    VMware
  • ISC
    ISC
  • SAP
    SAP
  • EMC
    EMC
  • PMI
    PMI
  • HP
    HP
  • Salesforce
    Salesforce
  1. Home
  2. ECCouncil Certification
  3. 312-96 Exam
  4. ECCouncil.312-96.v2024-07-23.q33 Dumps
  • «
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • 7
  • 8
  • »
Download Now

Question 21

In a certain website, a secure login feature is designed to prevent brute-force attack by implementing account lockout mechanism. The account will automatically be locked after five failed attempts. This feature will not allow the users to login to the website until their account is unlocked. However, there is a possibility that this security feature can be abused to perform __________ attack.

Correct Answer: A
insert code

Question 22

Which of the risk assessment model is used to rate the threats-based risk to the application during threat modeling process?

Correct Answer: C
insert code

Question 23

It is recommended that you should not use return, break, continue or throw statements in _________

Correct Answer: C
insert code

Question 24

Alice, a security engineer, was performing security testing on the application. He found that users can view the website structure and file names. As per the standard security practices, this can pose a serious security risk as attackers can access hidden script files in your directory. Which of the following will mitigate the above security risk?

Correct Answer: D
insert code

Question 25

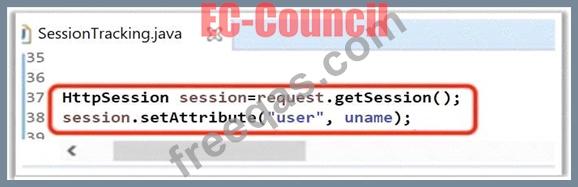
A developer has written the following line of code to handle and maintain session in the application. What did he do in the below scenario?

Correct Answer: A
The line of code in the scenario creates a session attribute named "user" with a value taken from the variable
"uname". This is a common practice in web applications to maintain state across multiple requests from the same user. In this instance, the HttpSession object is retrieved from the request object, and then it's used to store an attribute. By setting this session attribute, the developer ensures that the value stored in the variable uname can be associated with the user's session and retrieved during subsequent requests within the same session.
insert code
  • «
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • 7
  • 8
  • »
[×]

Download PDF File

Enter your email address to download ECCouncil.312-96.v2024-07-23.q33 Dumps

Email:

FreeQAs

Our website provides the Largest and the most Latest vendors Certification Exam materials around the world.

Using dumps we provide to Pass the Exam, we has the Valid Dumps with passing guranteed just which you need.

  • DMCA
  • About
  • Contact Us
  • Privacy Policy
  • Terms & Conditions
©2026 FreeQAs

www.freeqas.com materials do not contain actual questions and answers from Cisco's certification exams.