FreeQAs
 Request Exam  Contact
  • Home
  • View All Exams
  • New QA's
  • Upload
PRACTICE EXAMS:
  • Oracle
  • Fortinet
  • Juniper
  • Microsoft
  • Cisco
  • Citrix
  • CompTIA
  • VMware
  • ISC
  • SAP
  • EMC
  • PMI
  • HP
  • Salesforce
  • Other
  • Oracle
    Oracle
  • Fortinet
    Fortinet
  • Juniper
    Juniper
  • Microsoft
    Microsoft
  • Cisco
    Cisco
  • Citrix
    Citrix
  • CompTIA
    CompTIA
  • VMware
    VMware
  • ISC
    ISC
  • SAP
    SAP
  • EMC
    EMC
  • PMI
    PMI
  • HP
    HP
  • Salesforce
    Salesforce
  1. Home
  2. ECCouncil Certification
  3. 312-96 Exam
  4. ECCouncil.312-96.v2024-07-23.q33 Dumps
  • «
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • 7
  • 8
Download Now

Question 31

Oliver, a Server Administrator (Tomcat), has set configuration in web.xml file as shown in the following screenshot. What is he trying to achieve?

Correct Answer: A
The configuration set in the web.xml file as indicated by the <transport-guarantee> tag set to CONFIDENTIAL suggests that Oliver, the Server Administrator, is aiming to ensure that all data transmitted between the client and the server is done over an encrypted channel. This is a common security practice to protect sensitive data from being intercepted or tampered with during transmission. Here's how the setting works:
* Enforce HTTPS: The CONFIDENTIAL transport guarantee enforces the use of HTTPS, which encrypts the entire communication channel.
* Protect Data: By using HTTPS, not only are the session cookies protected, but all request and response data, including headers and parameters, are encrypted.
* Comply with Security Standards: This setting helps in complying with security standards and regulations that mandate encryption of sensitive data in transit.
References: The EC-Council Application Security Engineer (CASE) JAVA documentation and learning resources emphasize the importance of secure data transmission. The use of the CONFIDENTIAL setting in the web.xml file aligns with the best practices for securing web applications deployed on servers like Tomcat12. Additionally, the Java Servlet Specification provides guidelines on how to configure transport guarantees in the deployment descriptor (web.xml) to ensure secure data transmission.
insert code

Question 32

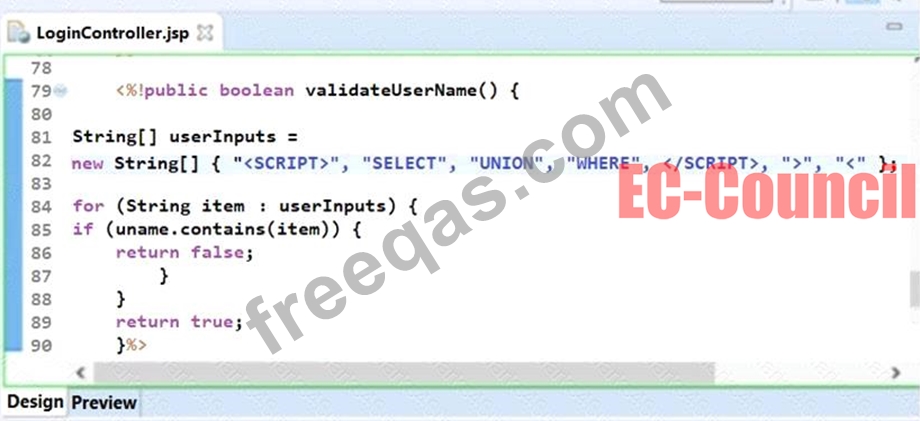
Sam, an application security engineer working in INFRA INC., was conducting a secure code review on an application developed in Java. He found that the developer has used a piece of code as shown in the following screenshot. Identify the security mistakes that the developer has coded?
Correct Answer: D
The code snippet provided is a Java method designed to validate usernames. It employs a blacklist input validation approach, where it checks if the username contains certain prohibited strings (like "SCRIPT",
"SELECT", "UNION", "WHERE", etc.). If the username contains any of these strings, the method returns false; otherwise, it returns true.
This approach is considered a security mistake because blacklisting is generally not as secure as whitelisting.
Blacklisting attempts to identify and block known bad inputs, but attackers can often bypass this by using variations or encodings that are not included in the blacklist. Whitelisting, on the other hand, only allows specifically approved inputs and blocks everything else, making it more secure.
In this specific case:
* The developer has created an array of strings containing SQL and script injection keywords.
* The validateUserName() function iteratively checks if any of these keywords are present in the username.
* If found, it returns false; otherwise true.
A more secure approach would be to use whitelist validation where only specific patterns of usernames are allowed or employ additional layers of security like parameterized queries or prepared statements to prevent SQL injection and encoding/escaping user inputs to prevent XSS attacks.
References:For precise references, please refer to the EC-Council's Certified Application Security Engineer (CASE) JAVA related courses and study guides, which provide comprehensive coverage on secure coding practices and input validation strategies1234.
insert code

Question 33

A
US-based ecommerce company has developed their website www.ec-sell.com to sell their products online.
The website has a feature that allows their customer to search products based on the price. Recently, a bug bounty has discovered a security flaw in the Search page of the website, where he could see all products from the database table when he altered the website URL http://www.ec-sell.com/products.jsp?val=100 to
http://www.ec-sell.com/products.jsp?val=200 OR
'1'='1 -. The product.jsp page is vulnerable to


Correct Answer: C
The vulnerability described allows an attacker to manipulate the query string in the URL to alter the SQL query executed by the server. This is a classic example of a SQL Injection attack, where the attacker inserts or
"injects" malicious SQL code into the query, which can lead to unauthorized access to database information.
The altered URL http://www.ec-sell.com/products.jsp?val=200
OR
'1'='1 is a typical SQL injection payload that forces the SQL query to return all products by making the WHERE clause always true ('1'='1).
To protect against SQL Injection attacks, developers should:
* Use Prepared Statements: These include parameterized queries that separate SQL logic from data, preventing attackers from modifying the SQL query.
* Employ Stored Procedures: They encapsulate the SQL logic on the server side and prevent exposure to SQL injection.
* Validate User Input: Ensure that all user-supplied data is validated for type, length, format, and range.
* Implement Error Handling: Avoid revealing detailed error messages that could give attackers clues about the database structure.
References: The EC-Council's Certified Application Security Engineer (CASE) Java documentation outlines the importance of secure coding practices to prevent common vulnerabilities like SQL Injection12. Additionally, the training materials cover various defensive programming techniques that are essential for creating secure Java applications, including those that prevent SQL Injection attacks345.
insert code
  • «
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • 7
  • 8
[×]

Download PDF File

Enter your email address to download ECCouncil.312-96.v2024-07-23.q33 Dumps

Email:

FreeQAs

Our website provides the Largest and the most Latest vendors Certification Exam materials around the world.

Using dumps we provide to Pass the Exam, we has the Valid Dumps with passing guranteed just which you need.

  • DMCA
  • About
  • Contact Us
  • Privacy Policy
  • Terms & Conditions
©2026 FreeQAs

www.freeqas.com materials do not contain actual questions and answers from Cisco's certification exams.