Which two actions must the administrator perform to allow FortiNAC-F to process incoming syslog messages from an unknown vendor? (Choose two.)
Correct Answer: A,B
An event parser must be created so FortiNAC-F can interpret and extract meaningful data from the unknown vendor's syslog messages. The sending device must be modeled in the Network Inventory so FortiNAC-F can associate the incoming syslog messages with a known device and properly process the generated events.
Question 7
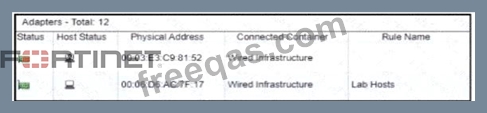
Refer to the exhibit. After a successful layer 2 poll, two hosts were learned on the same port The port is a member of the Role- Based Access and Forced Registration groups. The switch has been configured to leverage a single isolation VLAN. How will FortiNAC-F manage this port?
Correct Answer: A
The correct answer is A . The exhibit shows two adapters learned on the same wired port: one appears as a rogue/unknown host, and the other is associated with the Lab Hosts rule. The port is in both Role-Based Access and Forced Registration . FortiNAC-F state-based control takes precedence over policy-based provisioning, and the study guide states that when a rogue host connects to a port in the Forced Registration group, FortiNAC-F isolates that host by moving it into the registration captive network. The guide also explains that the Isolation network can be used as a single network for abnormal host states while still presenting state-specific portal pages. Because this is a wired switch port using VLAN-based control, FortiNAC-F cannot put one host on the production VLAN and the other host on the isolation portal VLAN at the same time on the same access port. The VLAN change applies to the port, not independently to each MAC address behind that port. Therefore, the presence of the rogue host on a Forced Registration port causes the port to be provisioned to the isolation network. Option B is technically unrealistic for this access-port scenario. Option C is wrong because two MAC addresses alone do not make the port an uplink; FortiNAC-F uses uplink logic for infrastructure-device MACs, manually marked uplinks, or a threshold such as more than 20 MAC addresses. Option D is unrelated because Access Point Management is not triggered by learning two wired hosts on a port.
Question 8
An administrator wants to continually monitor endpoints for the existence of a specific registry key and the status of a required security service. Which two requirements must be in place for the administrator to use FortiNAC-F compliance monitors? (Choose two.)
Correct Answer: C,D
Compliance monitors require the persistent agent to continuously evaluate endpoint conditions such as registry keys and service status. A custom scan must be defined to specify the exact registry key and security service checks that the monitor will assess on the endpoint.
Question 9
During an evaluation of state-based enforcement, an administrator discovers that ports that should not be under enforcement have been added to enforcement groups. In which view would the administrator be able to identify who added the ports to the groups?
Correct Answer: A
In FortiNAC-F, accountability and forensic tracking of configuration changes are managed through the Admin Auditing functionality. When an administrator performs an action that modifies the system state--such as creating a policy, changing a device's status, or adding a switch port to an Enforcement Group--the system generates an audit record. This record is essential for troubleshooting scenarios where unauthorized or accidental configuration changes have occurred, leading to unintended network behavior. The Admin Auditing view (found under Logs > Admin Auditing) provides a comprehensive log of the "Who, What, and When" for every administrative session. Each entry includes the username of the administrator, the source IP address from which they accessed the FortiNAC-F console, a precise timestamp, and a detailed description of the modification. In the scenario described, where port have been incorrectly added to enforcement groups, the Admin Auditing view allows a supervisor to filter by the specific "Port" or "Group" object to identify exactly which administrator executed the command.
Question 10
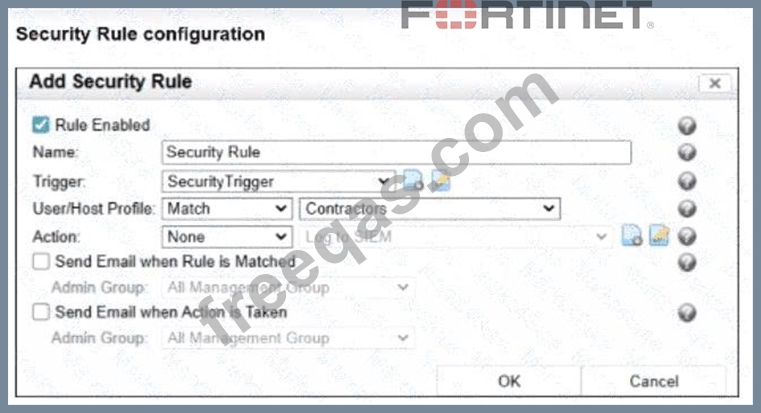
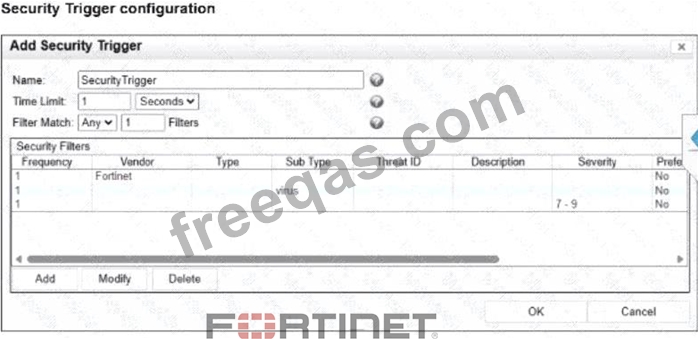
Refer to the exhibits. Given the current configuration, what would happen if a contractor triggered two of the defined security filters?
Correct Answer: B
The correct answer is B . In the trigger exhibit, the Filter Match setting is configured as Any 1 Filters , meaning the security trigger is satisfied when any one of the defined filters matches within the configured time window. The contractor triggers two of the defined filters, so two separate security events are generated because FortiNAC-F creates a security event whenever a security filter matches. The study guide confirms that each matched filter generates a security event, and when a trigger contains multiple filters, multiple matched filters can be associated with the resulting alarm. The security rule exhibit also shows User/Host Profile: Match Contractors . Because the triggering user is a contractor, the user/host profile condition is satisfied. Once the trigger is satisfied and the user/host profile matches, FortiNAC-F generates a security alarm . The fact that Action is set to None does not stop the alarm from being generated; it only means no automated or manual response action is executed from that rule. Option A is wrong because the contractor profile matches, so an alarm is generated. Option C is wrong because only two filters were triggered, not three. Option D is wrong because two filters matched, so two events are generated, not one. The exhibits show an enabled Security Rule using the SecurityTrigger , with the User/Host Profile configured as Match # Contractors . The associated trigger contains multiple security filters and uses Filter Match = Any . Because the endpoint in the scenario is a contractor, the User/Host Profile condition is satisfied. The critical FortiNAC-F distinction is between a security event and a security alarm . The Study Guide states that a security event is generated whenever a security filter evaluates as true . Therefore, if the contractor triggers two security filters, two separate security events are generated . The trigger is also satisfied, and because the Contractors profile matches, the security rule matches. A successful security-rule match generates one security alarm . The guide explicitly explains that a trigger can contain multiple filters and that each matched filter generates a security event; consequently, multiple events can be associated with a single alarm. The exhibit ' s Action = None does not suppress alarm creation-it only means no response action is executed. Therefore: 2 matched filters = 2 security events + 1 security alarm. Study Guide Reference: Security Device Integration and Automated Response - Security Rules, Security Events and Alarms, Security Triggers , pp. 328-333 .