FreeQAs
 Request Exam  Contact
  • Home
  • View All Exams
  • New QA's
  • Upload
PRACTICE EXAMS:
  • Oracle
  • Fortinet
  • Juniper
  • Microsoft
  • Cisco
  • Citrix
  • CompTIA
  • VMware
  • ISC
  • SAP
  • EMC
  • PMI
  • HP
  • Salesforce
  • Other
  • Oracle
    Oracle
  • Fortinet
    Fortinet
  • Juniper
    Juniper
  • Microsoft
    Microsoft
  • Cisco
    Cisco
  • Citrix
    Citrix
  • CompTIA
    CompTIA
  • VMware
    VMware
  • ISC
    ISC
  • SAP
    SAP
  • EMC
    EMC
  • PMI
    PMI
  • HP
    HP
  • Salesforce
    Salesforce
  1. Home
  2. Fortinet Certification
  3. NSE6_FNC_AD-7.6 Exam
  4. Fortinet.NSE6_FNC_AD-7.6.v2026-11-16.q53 Dumps
  • ««
  • «
  • …
  • 2
  • 3
  • 4
  • 5
  • 6
  • 7
  • 8
  • 9
  • 10
  • 11
  • …
  • »
  • »»
Download Now

Question 26

While troubleshooting a network connectivity issue, an administrator determines that a device was being automatically provisioned to an incorrect VLAN. Where would the administrator look to identify when and why FortiNAC-F made the network access change?

Correct Answer: C
The correct answer is C . The Port Changes view is the correct troubleshooting location when FortiNAC-F changes endpoint network access, such as moving a switch port into a different VLAN. The study guide states that any time FortiNAC-F changes network access for an endpoint, the change is documented in Network > Port Changes . This view shows the date and time of the change, whether a CLI configuration was executed, the reason for the change, the role or access policy that caused it, the port that was changed, and the VLAN the port was changed to.
This directly matches the troubleshooting requirement in the question: the administrator needs to know when the VLAN change happened and why FortiNAC-F made that network access decision. Option A , Security Event view, is used for security-related events, not detailed port-level VLAN-change history. Option B , Reports view, is too broad and not the operational audit trail for a specific access change. Option D , Admin Auditing, tracks administrative actions, but an automatic policy-driven VLAN assignment is documented under Port Changes, not primarily as an admin audit event.
insert code

Question 27

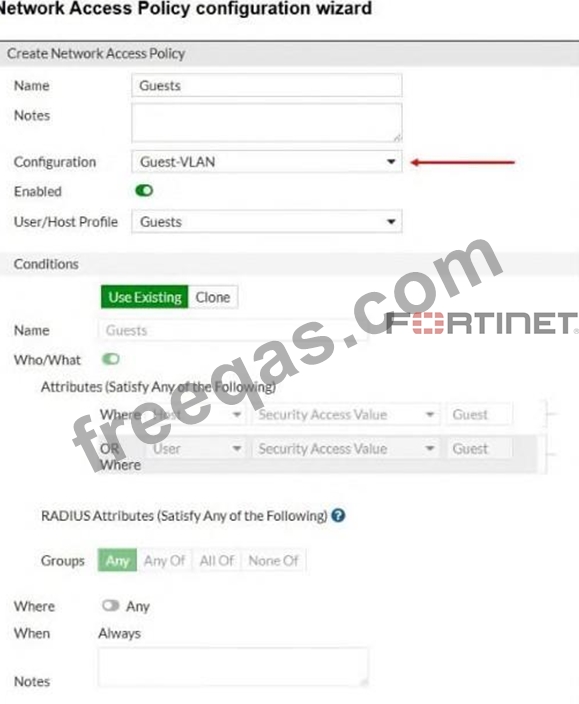
Refer to the exhibit.

When configuring guest access using a network access policy, where would an administrator configure the Guest-VLAN value?

Correct Answer: A
The Guest-VLAN value is defined within the switch Model configuration, where VLAN mappings and enforcement actions are configured. The network access policy references this configuration to apply the appropriate VLAN when the policy conditions are met.
insert code

Question 28

An administrator wants to use FortiNAC-F to prevent internal engineers from accessing specific websites as defined in web filter categories on FortiGate.
In addition to a security trigger and associated action, which configuration must also be defined on FortiNAC-F?

Correct Answer: D
To enforce restrictions based on web filter categories for internal engineers, FortiNAC-F must identify and group those users or their devices. A user/host profile defines the specific users or hosts (such as internal engineers) to which the security trigger and associated action will apply, enabling targeted enforcement.
insert code

Question 29

An administrator wants to create a conference manager administrator account but would like to limit the number of conference accounts that can be generated to 30. Which statement about conference accounts is true?

Correct Answer: D
In FortiNAC-F, the maximum number of conference attendees/accounts is controlled by the Guest & Contractor template , not by the sponsor's administrative profile. The FortiNAC-F 7.6 Administrator Study Guide states that conference accounts are initiated by a sponsor but automatically generated by FortiNAC-F, and specifically that "the maximum number of attendees is defined within the template." The Administration Guide provides the corresponding configuration field: Max Number Of Accounts , which is available when Visitor Type = Conference . Enabling this option allows the administrator to enter the maximum number of accounts that can ever be created using that template. Therefore, a value of exactly
30 can be configured; there is no requirement to use multiples of 25.
The administrative profile instead determines sponsor capabilities such as permitted account types, allowed templates, account-management scope, and maximum account duration. It does not define the numerical conference-account ceiling.
Thus, to enforce a limit of 30 conference accounts, configure Max Number Of Accounts = 30 in the conference Guest & Contractor template .
Study Guide Reference: Guest and Contractor Management # Creating Conference Accounts , pp. 292-302 .
insert code

Question 30

While troubleshooting a network connectivity issue, an administrator determines that a device was being automatically provisioned to an incorrect VLAN.
Where would the administrator look to identify when and why FortiNAC-F made the network access change?

Correct Answer: A
The Port Changes view records provisioning actions performed by FortiNAC-F, including VLAN changes, along with the associated reason and timestamp. This allows the administrator to determine when the network access change occurred and what triggered it.
insert code
  • ««
  • «
  • …
  • 2
  • 3
  • 4
  • 5
  • 6
  • 7
  • 8
  • 9
  • 10
  • 11
  • …
  • »
  • »»
[×]

Download PDF File

Enter your email address to download Fortinet.NSE6_FNC_AD-7.6.v2026-11-16.q53 Dumps

Email:

FreeQAs

Our website provides the Largest and the most Latest vendors Certification Exam materials around the world.

Using dumps we provide to Pass the Exam, we has the Valid Dumps with passing guranteed just which you need.

  • DMCA
  • About
  • Contact Us
  • Privacy Policy
  • Terms & Conditions
©2026 FreeQAs

www.freeqas.com materials do not contain actual questions and answers from Cisco's certification exams.