FreeQAs
 Request Exam  Contact
  • Home
  • View All Exams
  • New QA's
  • Upload
PRACTICE EXAMS:
  • Oracle
  • Fortinet
  • Juniper
  • Microsoft
  • Cisco
  • Citrix
  • CompTIA
  • VMware
  • ISC
  • SAP
  • EMC
  • PMI
  • HP
  • Salesforce
  • Other
  • Oracle
    Oracle
  • Fortinet
    Fortinet
  • Juniper
    Juniper
  • Microsoft
    Microsoft
  • Cisco
    Cisco
  • Citrix
    Citrix
  • CompTIA
    CompTIA
  • VMware
    VMware
  • ISC
    ISC
  • SAP
    SAP
  • EMC
    EMC
  • PMI
    PMI
  • HP
    HP
  • Salesforce
    Salesforce
  1. Home
  2. Fortinet Certification
  3. NSE6_FNC_AD-7.6 Exam
  4. Fortinet.NSE6_FNC_AD-7.6.v2026-11-16.q53 Dumps
  • «
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • 7
  • 8
  • 9
  • 10
  • …
  • »
  • »»
Download Now

Question 16

In which three ways would deploying a FortiNAC-F Manager into a large environment consisting of several FortiNAC-F CAs simplify management? (Choose three.)

Correct Answer: B,D,E
The FortiNAC-F Manager (FortiNAC-M) is designed as a centralized management platform for large- scale distributed environments where multiple FortiNAC-F Control and Application (CA) appliances are deployed across different sites. According to the FortiNAC-F Manager Administration Guide, the deployment of a Manager simplifies administrative overhead in three specific ways:
First, it provides Global Version Control (B). The Manager serves as a central repository for firmware and software updates, allowing administrators to push specific versions to all managed CAs simultaneously, ensuring consistency across the entire fabric. Second, it enables Pooled Licenses (D). Instead of purchasing and managing individual licenses for every CA, licenses are centralized on the Manager. The Manager then distributes these licenses to the CAs as needed based on their host counts. This "floating" license model optimizes cost and prevents individual sites from running out of capacity while others have excess. Third, it offers Global Visibility (E).
The Manager aggregates host and device data from every managed CA into a single console.
This "single pane of glass" allows an administrator to search for a specific MAC address or user across the entire global organization without logging into individual servers.
insert code

Question 17

An administrator wants to build a security rule that will quarantine contractors who attempt to access specific websites.
In addition to a user host profile, which two components must the administrator configure to create the security rule? (Choose two.)

Correct Answer: B,D
A security rule requires a trigger to detect the condition, such as contractors accessing specific websites based on security or traffic events. It also requires an action to define the response, such as quarantining the contractor when the trigger condition is met.
insert code

Question 18

A network administrator is troubleshooting a network access issue for a specific host. The administrator suspects the host is being assigned a different network access policy than expected.
Where would the administrator look to identify which network access policy, if any, is being applied to a particular host?

Correct Answer: C
When troubleshooting network access in FortiNAC-F, it is often necessary to verify exactly why a host has been granted a specific level of access. Since FortiNAC-F evaluates policies from the top down and assigns access based on the first match, an administrator needs a clear way to see the results of this evaluation for a specific live endpoint.
The Policy Details (C) view is the designated tool for this purpose. By navigating to the Hosts > Hosts (or Adapter View) in the Administration UI, an administrator can search for the specific MAC address or IP of the host in question. Right-clicking on the host record reveals a context menu from which Policy Details can be selected. This view provides a real-time "look" into the policy engine's decision for that specific host, showing the Network Access Policy that was matched, the User/Host Profile that triggered the match, and the resulting Network Access Configuration (VLAN/ACL) currently applied.
insert code

Question 19

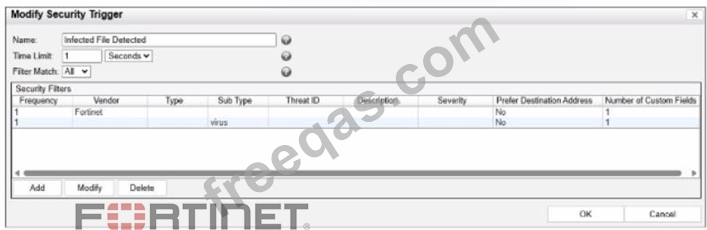
Refer to the exhibit. What would FortiNAC-F generate if only one of the security fitters is satisfied?
Correct Answer: D
In FortiNAC-F, Security Triggers are used to identify specific security-related activities based on incoming data such as Syslog messages or SNMP traps from external security devices (like a FortiGate or an IDS). These triggers act as a filtering mechanism to determine if an incoming notification should be escalated from a standard system event to a Security Event.
According to the FortiNAC-F Administrator Guide and relevant training materials for versions 7.2 and 7.4, the Filter Match setting is the critical logic gate for this process. As seen in the exhibit, the "Filter Match" configuration is set to "All". This means that for the Security Trigger named
"Infected File Detected" to "fire" and generate a Security Event or a subsequent Security Alarm, every single filter listed in the Security Filters table must be satisfied simultaneously by the incoming data.
In the provided exhibit, there are two filters: one looking for the Vendor "Fortinet" and another looking for the Sub Type "virus". If only one of these filters is satisfied (for example, a message from Fortinet that does not contain the "virus" subtype), the logic for the Security Trigger is not met. Consequently, FortiNAC-F does not escalate the notification. Instead, it processes the incoming data as a Normal Event, which is recorded in the Event Log but does not trigger the automated security response workflows associated with security alarms.
"The Filter Match option defines the logic used when multiple filters are defined. If 'All' is selected, then all filter criteria must be met in order for the trigger to fire and a Security Event to be generated. If the criteria are not met, the incoming data is processed as a normal event. If 'Any' is selected, the trigger fires if at least one of the filters matches."
insert code

Question 20

Refer to the exhibits.


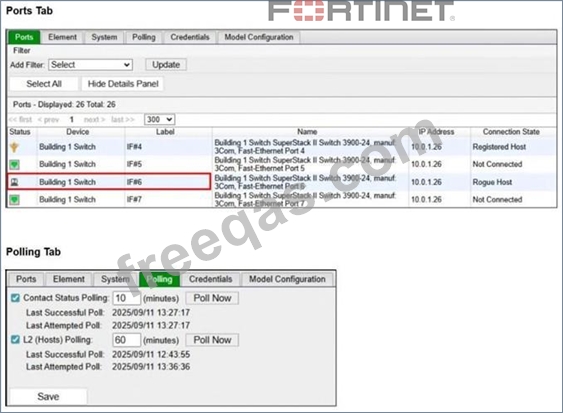
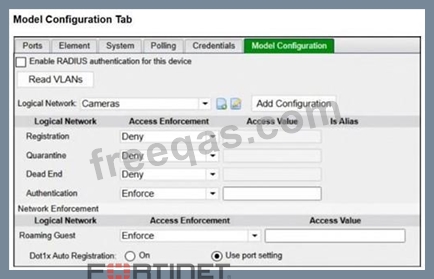
An administrator is troubleshooting visibility issues on a modeled switch. The switch is configured to use link traps and to provision hosts based on network access policies. The administrator is seeing hosts on ports with no hosts connected and not seeing hosts on ports where hosts are known to be connected.
What is the most likely cause?

Correct Answer: B
Incorrect switch credentials prevent FortiNAC-F from successfully performing SNMP-based polling (such as layer 2 host learning) needed to accurately learn and clear hosts per port. As a result, FortiNAC-F displays stale or missing host-to-port associations even though link traps are enabled.
insert code
  • «
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • 7
  • 8
  • 9
  • 10
  • …
  • »
  • »»
[×]

Download PDF File

Enter your email address to download Fortinet.NSE6_FNC_AD-7.6.v2026-11-16.q53 Dumps

Email:

FreeQAs

Our website provides the Largest and the most Latest vendors Certification Exam materials around the world.

Using dumps we provide to Pass the Exam, we has the Valid Dumps with passing guranteed just which you need.

  • DMCA
  • About
  • Contact Us
  • Privacy Policy
  • Terms & Conditions
©2026 FreeQAs

www.freeqas.com materials do not contain actual questions and answers from Cisco's certification exams.