An organization wants to add a FortiNAC-F Manager to simplify their large FortiNAC-F deployment. Which two policy types can be managed globally? (Choose two.)
Correct Answer: A,D
A FortiNAC-F Manager allows centralized management of authentication policies so user and device authentication behavior is consistent across all managed CAs. It also supports global network access policies, enabling uniform access control and enforcement logic to be applied throughout the entire deployment from a single management point.
Question 37
Which two requirements must be met to set up an N+1 HA cluster? (Choose two.)
Correct Answer: A,B
TheN+1 High Availability (HA)architecture was introduced in FortiNAC-F version 7.6 to provide a more scalable and flexible redundancy model compared to the traditional 1+1 active/passive setup. In an N+1 configuration, a single secondary (standby) appliance can provide coverage for multiple primary (active) Control and Application (CA) appliances. To set up an N+1 HA cluster, there are two fundamental structural requirements: A FortiNAC-F Manager (FortiNAC-M):Unlike standard 1+1 HA, which can be configured directly between two CAs, N+1 management is centralized. The FortiNAC-M acts as the orchestrator that manages the failover groups, monitors the health of the primaries, and coordinates the promotion of the secondary server if a primary fails. A FortiNAC-F device designated as a Secondary:The cluster must have one appliance explicitly configured with theSecondary failover role. This device remains in a standby state, receiving database replications from all N primaries in its group until it is called upon to take over the functions of a failed unit. While a cluster can support multiple primaries (D), it does not strictly require " at least two " to function as an N+1 group; it simply requires N primaries (where N # 1). Additionally, N+1 is typically a Layer 3 managed solution via the Manager, meaning it does not mandate a " dedicated VLAN " for synchronization like some Layer 2 HA deployments. " In FortiNAC-F 7.6,FortiNAC-Mfunctions as a manager to manage the N+1 Failover Groups... enabling N+M high availability for CAs. To create an N+1 Failover group, you should add thesecondary CAto the FortiNAC-M first, then add the primary CAs. The secondary CA is designed to take over the functionality of any single failed primary component. " -FortiNAC-F 7.6.0 N+1 Failover Reference Manual.
Question 38
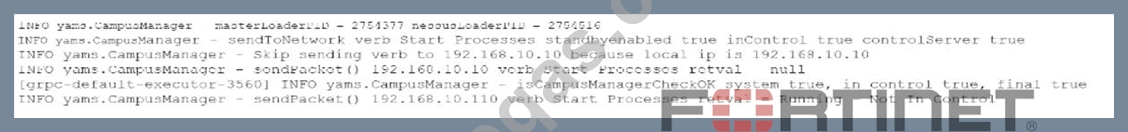
Refer to the output below. Examine the communication between a primary FortiNAC-F (192.168.10.10) and a secondary FortlNAC-F (192.168.10.110) configured as a 1+1 HA pair. What is the current state of the FortiNAC-F HA pair?
Correct Answer: D
The correct answer is D . The log output shows the local IP address as 192.168.10.10 , which the question identifies as the primary FortiNAC-F server. In the same output, FortiNAC-F reports inControl true and controlServer true , which means the local primary server is currently the control server. The line showing communication to 192.168.10.110 returns Running - Not In Control , confirming that the secondary server is alive but is not the active controlling node. This matches FortiNAC-F 1+1 HA behavior. The study guide describes a 1+1 HA pair as an active-passive deployment where one FortiNAC-F device is designated primary and the other secondary. Database and configuration synchronization keep the devices aligned, but only one server is in control at a time. If the primary fails, the secondary assumes control automatically; otherwise, the primary remains the active control server. Option A is wrong because the secondary explicitly reports Not In Control . Option B is wrong because the output does not show database replication failure. Option C is wrong because failover is not in progress; the output shows a stable state where the primary is in control and the secondary is running as the passive node.
Question 39
Two FortiNAC-F devices have been configured as a 1+1 HA pair. The primary server went offline and a successful failover to the secondary has occurred. What happens if the primary server comes back online?
Correct Answer: D
In a 1+1 HA configuration, once failover has occurred and the secondary assumes control, it remains the active controller when the original primary comes back online. The restored primary rejoins as the standby unit, and control is not automatically reverted.
Question 40
When preparing network infrastructure devices for visibility, what are the two main advantages of using MAC notification traps on supported devices instead of link-up and link-down traps? (Choose two.)
Correct Answer: B,C
Comprehensive and Detailed Explanation From Exact Extract of FortiNAC-F 7.6 Administrator Guide or Knowledge: Exact Extract: The FortiNAC-F study guide states that MAC notification traps are preferred because FortiNAC-F does not need to connect back to the infrastructure device every time a link-up or link-down trap is received. The required MAC and port information is already included in the MAC notification trap, which makes database updates faster and uses fewer resources. It also states that hosts and devices connected through hubs or IP phones are seen immediately, even when the downstream device cannot generate link-up or link-down traps. Technical Deep Dive: The correct answers are B and C . With link-up/link-down traps, the trap only tells FortiNAC-F that an interface changed state. FortiNAC-F then has to perform an L2 poll against the switch forwarding table to discover which MAC address appeared or disappeared. That means extra SNMP/CLI activity, more delay, and more processing on both FortiNAC-F and the switch. The guide confirms that link traps trigger FortiNAC- F to perform a Layer 2 poll, while MAC notification traps directly contain the learned or removed MAC address and associated port. Option A is wrong because MAC notification traps are Layer 2 visibility events. They identify MAC address and port , not IP address. IP-to-MAC correlation comes from Layer 3 polling or DHCP fingerprinting, not MAC notification traps. Option D is badly worded and should not be selected: MAC notification traps do provide faster updates, but the processing overhead is reduced, not slightly increased. Operationally, on supported switches you enable SNMP traps for MAC address-table changes and point the trap destination to FortiNAC-F. On Cisco-style infrastructure, this is usually done with commands such as snmp-server host < FortiNAC-IP > version 2c < community > plus MAC notification trap configuration. Do not enable MAC notification traps on uplinks, because uplinks learn many downstream MAC addresses and would create misleading endpoint-location data.