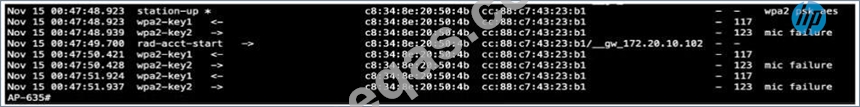
A customer has deployed anAOS 10 mobilitygateway cluster consisting of three controllers at a single site The WLAN is configured to tunnel wireless device traffic to the AOS 10 mobilitycluster.The clients areauthorized to use WPA2-Personal.An end-userhas opened a ticket with the helpdesk stating they cannot connect their client device to the network.There are other devices currently associated with the SSID with no issues. Reviewing the output, what Is the issue?
Correct Answer: C
The issue indicated by the output is an invalid pre-shared key (PSK). The logs show multiple failures during the WPA2 key exchange process, which points to a mismatch between the PSK configured on the client device and the PSK expected by the AOS 10 mobility gateway.
Question 57
Your customer asked for help to apply an ACL for wireless guest users with the following criteria: * Wi-Fi guests are on VLAN 555 * allow internet access * only allow access to public DNS servers * deny access to all internal networks except for any DHCP server These session ACLs are already present in the CLI of the mobility gateway group: You have access to the CLl. Which user role meets all the criteria?
Correct Answer: A
Based on the criteria provided for wireless guest users, the correct user role configuration must allow internet access, only allow access to public DNS servers, deny access to all internal networks except for any DHCP server, and place the Wi-Fi guests on VLAN 555. The ACLs must permit services necessary for basic internet access (such as DNS and DHCP) and block access to internal networks. Option A satisfies these criteria with the following configurations: * user-role "WiFi-guest": This defines the role for Wi-Fi guests. * access-list session dhcp-acl: This applies the access list that likely permits DHCP, which is necessary for guests to obtain an IP address. * access-list session dns-acl: This applies the DNS access list, which likely restricts guests to using public DNS servers. * access-list session internal-networks: This applies the internal networks access list, which denies access to internal networks. * vlan 555: This sets the VLAN for Wi-Fi guests to 555. Options B, C, and D are incorrect because they include access-list session allowall which would permit all traffic, contradicting the requirement to deny access to all internal networks.
Question 58
After onboarding three new AOS-10 gateways using the full-setup method into the same HPE Aruba Networking Central group, a customer cannot log in to one of the gateways using the HPE Aruba Networking Central remote console due to an incorrect password. What is causing this issue?
Correct Answer: D
Comprehensive and Detailed Explanation From Exact Extract of HPE Aruba Networking Switching: When an AOS-10 gateway is onboarded into Aruba Central using the Full-Setup method, a local admin password is defined during the setup wizard on the gateway itself. Later, when the gateway joins an existing Aruba Central group, the group-level configuration (which includes the admin password defined for that group) is automatically pushed down to all devices in that group for configuration consistency. However, if the password defined during full-setup is different from the admin password defined in the Aruba Central group, the synchronization process can cause a mismatch between the local device password and the one expected by Central. This mismatch prevents remote console login from working properly because Aruba Central attempts to authenticate to the gateway using the group-level admin credentials, not the local credentials from full-setup. Exact Extract from HPE Aruba Networking Switching and Aruba Central Configuration Documents: "During onboarding, the admin password configured at the group level in Aruba Central is applied to all devices in the group. If a device is added using full-setup with a different password, it may fail Central- initiated authentication functions such as remote console." "When gateways are provisioned using the full-setup workflow, the local administrator password must match the group-level administrator credentials in Aruba Central to allow remote console and CLI access through Central." Therefore, the issue arises because the full-setup password for the gateway does not match the group admin password defined in Aruba Central, resulting in the 'incorrect password' error when attempting to access the gateway remotely through Central. Why the Other Options Are Incorrect: * A. The full-setup admin password is valid for remote access; there is no separate configuration option that "allows" or "disallows" remote console use. "Remote console access uses the same admin account configured for device login; there is no additional enablement required." * B. Aruba Central admin passwords do not expire by default. Group-level admin credentials are persistent configuration items, not time-based credentials. "Local and group administrator passwords are static until manually changed." * C. There is no "global Aruba Central admin password" used to authenticate to devices; authentication is performed using per-group or per-device credentials configured in Central. "Each Aruba Central group maintains its own admin credentials that are propagated to member devices; there is no single global password for all groups." References of HPE Aruba Networking Switching Documents or Study Guide: * ArubaOS 10.5.0 Gateway Deployment and Configuration Guide - "Onboarding using Full Setup" and "Group-Level Configuration Synchronization." * Aruba Central Device Management Guide - "Group Admin Credentials and Remote Console Access." * Aruba AOS 10 Campus Gateway Installation and Setup Guide - "Matching Group Admin Passwords for Central-Managed Devices."